OpenAI builds and deploys advanced AI models like GPT-4o for autonomous agents and workflows.
AgentScan
$59Starting price
0Popularity
About AgentScan
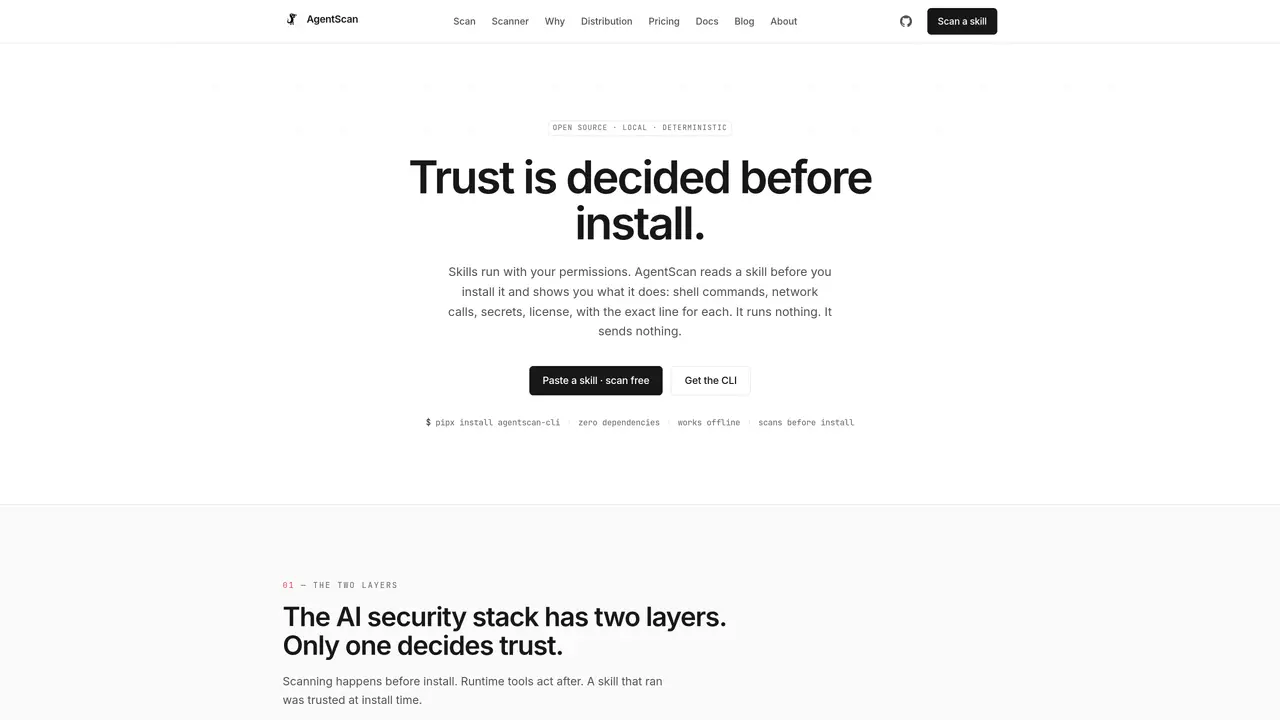
AgentScan is a local-first security scanner designed to inspect AI agent skills before they are installed. It operates entirely offline and executes nothing, providing deterministic reports on shell commands, network calls, secrets, licenses, and other potential risks. The tool reads skill metadata and code to surface findings with exact file and line references, allowing users to make informed trust decisions prior to execution. It supports scanning local directories, GitHub repositories, and individual skill files, outputting results in human-readable or JSON formats. AgentScan is aimed at developers and organizations using AI coding agents such as Claude Code, OpenAI Codex, OpenCode, Hermes, or Grok Build. Typical use cases include vetting third-party skills, auditing internal repositories, and ensuring compliance with security policies before deployment. The scanner is open-source and MIT licensed, with no account or telemetry required.
Key features
- Scans shell commands, network calls, and secrets
- Detects license declarations and missing licenses
- Outputs findings with file and line references
- Supports local directories and GitHub repositories
- Works with multiple AI agent runtimes
- Provides human-readable and JSON reports
- Includes severity-based risk summaries
- Supports SARIF output format
Use cases
- Vetting third-party AI agent skills before installation
- Auditing internal repositories for security risks
- Ensuring compliance with security policies in development environments
Pros
- Local and offline operation with no telemetry
- Deterministic, reproducible scans with exact line references
- Supports multiple AI coding agent runtimes
- Open-source and MIT licensed
- Human-readable and JSON output formats
Cons
- Trust Pack requires a one-time purchase
- No free tier for Trust Pack
- Limited to pre-install security checks
- No cloud-based scanning option
Frequently asked questions about AgentScan
What does AgentScan do?
AgentScan is a local-first security scanner that inspects AI agent skills before installation to identify potential risks such as shell commands, network calls, secrets, and licenses. It operates entirely offline, executes nothing, and provides deterministic reports with exact file and line references.
Who should use AgentScan?
AgentScan is designed for developers and organizations using AI coding agents like Claude Code, OpenAI Codex, OpenCode, Hermes, or Grok Build. It is particularly useful for vetting third-party skills, auditing internal repositories, and ensuring compliance with security policies before deployment.
How does AgentScan pricing work?
The AgentScan CLI is free and open-source, with no subscription required. Trust Pack, a professional skill bundle, is available as a one-time purchase with no recurring fees.
What integrations does AgentScan support?
AgentScan supports scanning local directories, GitHub repositories, and individual skill files. It also integrates with AI coding agents like Claude Code, OpenAI Codex, OpenCode, Hermes, and Grok Build through Trust Pack.
What are the limitations of AgentScan?
AgentScan does not execute skills or make trust decisions for users; it only provides reports. Findings are based on observed patterns and require manual review. It does not monitor skills after installation or prevent runtime issues.
How do I get started with AgentScan?
To get started, install the AgentScan CLI using pipx with the command 'pipx install agentscan-cli'. Then, scan a skill directory with 'agentscan scan .' for local scans or use other commands to search, install Trust Pack, or verify installed packages.