OpenAI builds and deploys advanced AI models like GPT-4o for autonomous agents and workflows.
CybeDefend
$18Starting price
1.5KMonthly visits
3Popularity
About CybeDefend
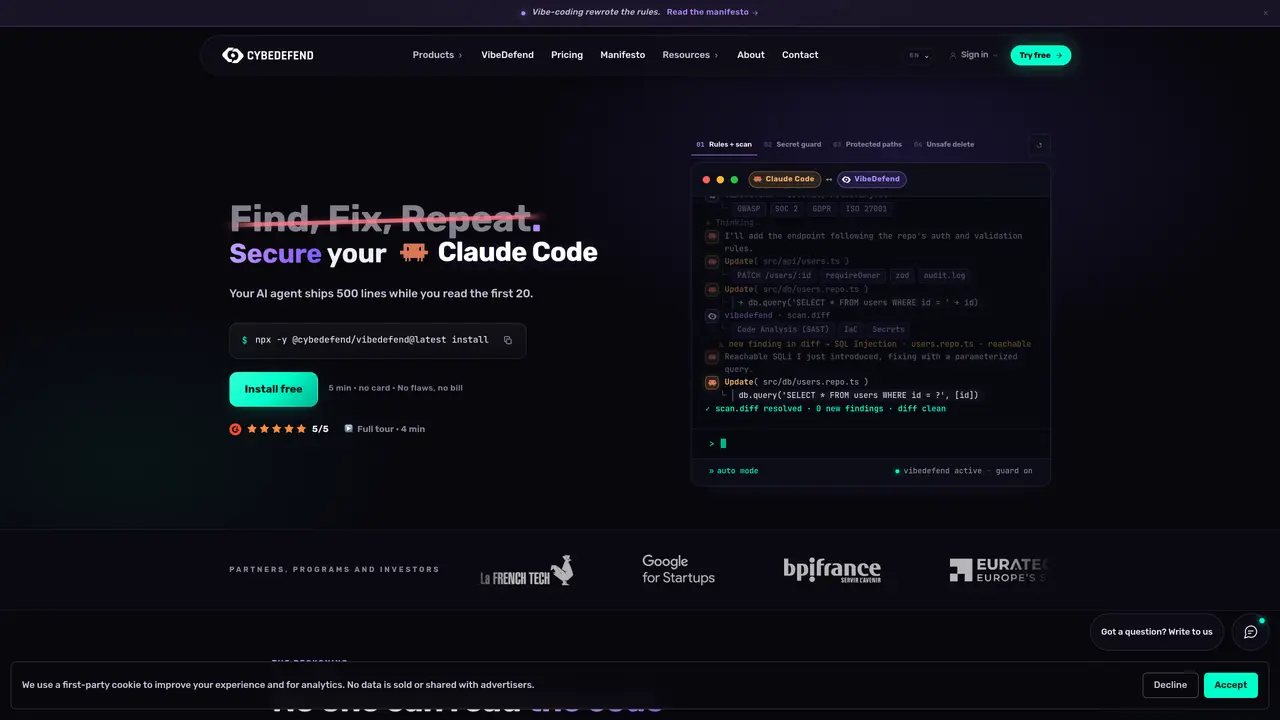
CybeDefend is a web-based SaaS application security testing (AST) platform designed for developers, AppSec teams, DevOps, and CISOs. It detects, prioritizes, and fixes vulnerabilities across the software development lifecycle by aggregating results from SAST, DAST, SCA, and Cybe Analysis. The platform provides a unified vulnerability dashboard that correlates findings and dependencies to streamline risk assessment. CybeDefend uses AI agents to assist with triage by sorting vulnerabilities by exploitability, relevance, and technical context, and can mark likely false positives as ignored with explanatory comments. Automated remediation is supported through Cybe AutoFix, which generates AI-powered pull requests to address vulnerabilities in source code and dependencies. The tool integrates with developer workflows via APIs and supports popular platforms such as GitHub, GitLab, Jenkins, Jira, Docker, VSCode, and IntelliJ/JetBrains, offering in-IDE guidance and fixes. It also includes a context-aware Security Champion assistant to provide tailored security guidance within developer workflows.
Key features
- Unified vulnerability dashboard aggregating SAST, DAST, SCA, and Cybe Analysis results
- AI-assisted triage with sorting by exploitability, relevance, and risk signals
- AI agents to review SAST findings and flag likely false positives
- Automated remediation via AI-generated pull requests
- Developer workflow integrations (GitHub, GitLab, Jenkins, Jira, Docker)
- IDE assistance with in-IDE guidance and fixes (VSCode, IntelliJ/JetBrains)
- Context-aware Security Champion assistant for tailored security guidance
- Cross-analysis to correlate findings and dependencies
Use cases
- Detecting and prioritizing vulnerabilities in source code and dependencies
- Automating security fixes via AI-generated pull requests
- Providing in-IDE security guidance and remediation for developers
Pros
- Aggregates and correlates results from multiple security testing methods (SAST, DAST, SCA, and custom analysis) into a unified vulnerability dashboard
- Uses AI agents to triage vulnerabilities by exploitability, relevance, and technical context, reducing manual review workload
- Provides automated remediation through AI-powered pull requests (Cybe AutoFix) to address vulnerabilities directly in source code and dependencies
- Integrates seamlessly with developer workflows via APIs and supports popular platforms such as GitHub, GitLab, Jenkins, Jira, Docker, VSCode, and IntelliJ/JetBrains
- Includes a context-aware Security Champion assistant to deliver tailored security guidance within developer environments
Cons
- May require initial setup and configuration to align with specific business rules and compliance frameworks
- Dependent on the accuracy of the AI agents' triage and remediation suggestions, which could occasionally misclassify vulnerabilities
- Continuous scanning and graph-based indexing may introduce overhead in resource-intensive development environments
Frequently asked questions about CybeDefend
What is CybeDefend and what does it do?
CybeDefend is an agent-time Application Security Testing (AST) platform designed to secure AI coding agents by detecting, prioritizing, and fixing vulnerabilities in real time. It integrates with AI coding environments to provide continuous scanning, false-positive filtering, and automated remediation through AI-powered pull requests.
Who is CybeDefend designed for?
The platform is designed for developers, AppSec teams, DevOps engineers, and CISOs who need to secure AI-generated code and enforce business logic and compliance rules within their development workflows.
How does CybeDefend integrate with AI coding tools?
CybeDefend integrates directly with AI coding agents like Claude Code, Cursor, Windsurf, Copilot, and Codex, providing real-time security checks and remediation suggestions within the agent's workflow.
Does CybeDefend require manual rule configuration?
No, CybeDefend's Autopilot feature automatically drafts security rules by analyzing your code graph, eliminating the need for manual rule writing or a dedicated security engineer.
What types of vulnerabilities does CybeDefend detect?
CybeDefend detects vulnerabilities that traditional scanners often miss, such as business logic flaws, multi-tenant leaks, refund bypasses, and missing idempotency, by leveraging a context-aware security knowledge graph.
How does CybeDefend handle false positives?
CybeDefend filters false positives by continuously scanning code changes and using its security knowledge graph to assess reachability and relevance, reducing noise before vulnerabilities reach developers.
CybeDefend Website Engagement
Last Update: 9 days ago
Total Monthly Visits
0
Bounce Rate
0%
Visit Duration (avg)
0.00s
Pages Per Visit
0
Country Rank
—
Unknown
Global Rank
0