Automates open source vulnerability detection and delivers immediate patches.
Amplify Security
FreeStarting price
0Popularity
About Amplify Security
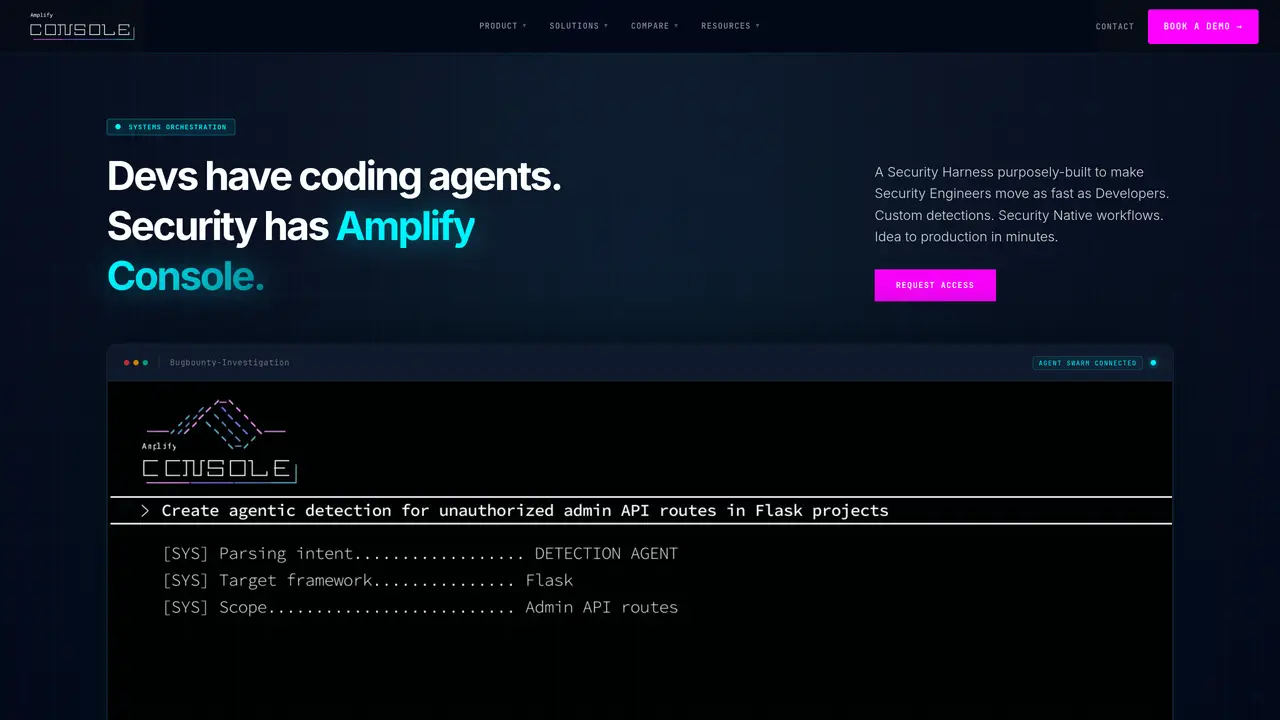
Amplify Security provides an agentic security harness designed to transform how security teams operate by moving at the speed of development. The platform replaces generic coding agents with purpose-built infrastructure that understands security workflows, enabling teams to create, deploy, and orchestrate custom detection agents tailored to their specific needs. Unlike traditional security tools that rely on prescriptive detections, Amplify Console allows security engineers to spring up agents that map relationships across codebases and prioritize issues based on actual reachability and exploitability. The system integrates directly into existing pipelines, pushing custom detections and automated fixes into CI/CD workflows with minimal disruption. A centralized operational cockpit provides visibility and control over every agent, detection, and remediation, shifting the focus from chasing endless vulnerabilities to orchestrating continuous, context-aware security. The platform is built to elevate any environment, helping teams solve the issues that matter most while maintaining development velocity and reducing reliance on specialized security expertise.
Key features
- AI-powered vulnerability detection in source code
- Automatic generation of code fixes
- One-click remediation via GitHub or GitLab pull requests
- Seamless integration with existing development workflows
- Reduces vulnerability remediation time from months to minutes
- Eliminates need for specialized security expertise
- Automates security compliance processes
- Maintains development velocity without disruption
Use cases
- Automating security compliance in software development
- Reducing manual effort in vulnerability remediation
- Integrating security checks into CI/CD pipelines
Pros
- Purpose-built agentic security infrastructure designed specifically for security workflows, not a generic AI wrapper
- Enables creation, deployment, and orchestration of custom detection agents in minutes
- Provides security-native context with deep visibility into codebases and relationships
- Supports one-click automated remediation directly integrated into CI/CD pipelines
- Offers a centralized operational cockpit for managing all agents, detections, and remediations
Cons
- Requires application for access, which may delay immediate adoption
- Limited to environments where custom agentic detections are applicable and valuable
- May not replace all traditional security scanning tools for organizations with complex legacy systems
Frequently asked questions about Amplify Security
What does Amplify Security do?
Amplify Security provides an agentic security harness that enables teams to create, deploy, and orchestrate custom detection agents for identifying and remediating vulnerabilities in code. It integrates directly into development workflows to push automated fixes and orchestrate security operations from a centralized cockpit.
Who is Amplify Security designed for?
The platform is designed for security teams, including security engineers and CISOs, who need to move as fast as developers while maintaining robust security postures. It suits organizations looking to automate security compliance and reduce the time spent on manual vulnerability remediation.
How does Amplify Security integrate with existing tools?
Amplify Console integrates with source control systems, CI/CD pipelines, cloud environments, and ticketing systems. It elevates existing security tools by adding custom agentic detections and automated remediation capabilities tailored to specific environments.
What makes Amplify Security different from traditional security scanners?
Unlike traditional scanners that rely on prescriptive detections, Amplify Console enables the creation of custom detection agents that understand an organization's specific priorities and context. It focuses on issues that are actually reachable or exploitable, reducing false positives and prioritizing meaningful vulnerabilities.
How do I get started with Amplify Security?
Prospective users must apply for access through the website. Once approved, a dedicated engineer reviews the use case and provides access to the platform, including the operational cockpit and integration setup.
Does Amplify Security require specialized security expertise to use?
The platform is designed to reduce the need for specialized security expertise by automating much of the detection and remediation process. However, some familiarity with security workflows and CI/CD pipelines is beneficial for optimal use.