OpenAI builds and deploys advanced AI models like GPT-4o for autonomous agents and workflows.

Vibe Code Detector
$5Starting price
3.1KMonthly visits
8Popularity
About Vibe Code Detector
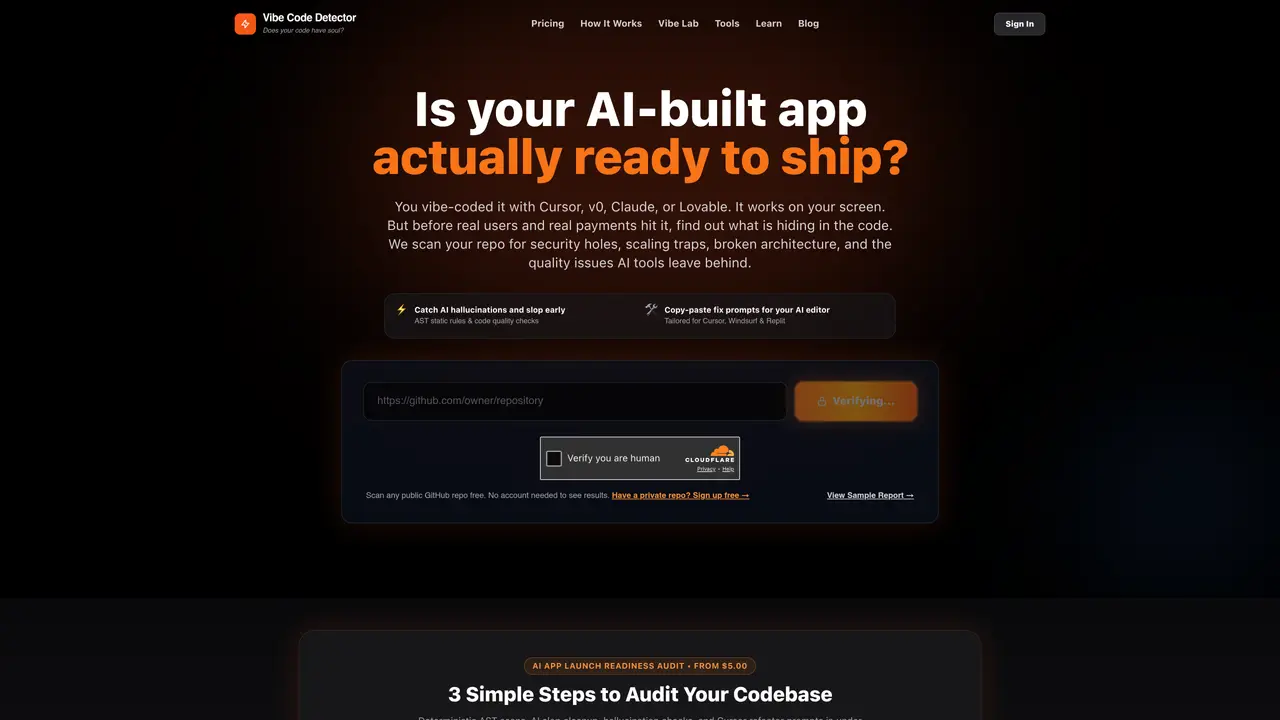
Vibe Code Detector performs static analysis and multi-layer AI synthesis to evaluate codebases built with AI assistants such as Cursor, Windsurf, v0, and Claude Code. It scans repositories for security vulnerabilities, supply chain risks, code quality issues, and AI-specific problems like hallucinated packages or token loops before customer launch. The tool provides evidence-backed findings with source line numbers, code diffs, and copy-paste refactor prompts tailored for Cursor, Windsurf, Replit, and Claude Code. Users submit a GitHub repository URL and receive an instant report with prioritized fixes and a free rescan within 14 days to verify corrections. The analysis avoids executing customer code or running package scripts, relying on deterministic AST rules and secure third-party AI providers with zero-retention policies. It is designed to address the unique patterns and pitfalls introduced by agentic AI coding workflows, including swallowed exceptions, unhandled promise rejections, and non-existent SDK method hallucinations.
Key features
- OWASP ASVS 4.0 security audit
- Supply chain and CVE inspection
- Code quality and cognitive complexity measurement
- AI code vibe score evaluation
- Copy-paste refactor prompts for AI editors
- Zero secret exposure policy for private code
- Instant AST static analysis under 10 seconds
- Evidence-backed report with source line numbers
Use cases
- Auditing AI-built applications before customer launch
- Identifying security vulnerabilities in AI-generated code
- Cleaning up AI slop and hallucinations in repositories
Pros
- Scans for OWASP ASVS 4.0 security flaws and hardcoded credentials
- Detects AI-specific issues like hallucinated packages and token loops
- Provides copy-paste refactor prompts for Cursor, Windsurf, Replit, and Claude Code
- Includes one free rescan within 14 days of the initial audit
- Supports both public and private GitHub repositories
Cons
- No free tier for full repository audits
- Requires GitHub repository submission
- Limited to one rescan per paid audit
- Pricing model is pay-per-repository
Frequently asked questions about Vibe Code Detector
What is an AI App Launch Readiness Audit?
An evidence-backed security and code quality review designed specifically for apps built with AI tools like Cursor, Windsurf, Replit Agent, v0, Claude Code, and Codex. It identifies OWASP security vulnerabilities, exposed secrets, cognitive complexity debt, and package CVEs before customer launch.
How does the codebase audit work?
When you submit a public or private GitHub repo, the engine runs deterministic AST static analysis rules combined with multi-layer AI synthesis to evaluate code quality, security vulnerabilities, and package debt before customer launch.
How is my private source code protected?
The tool enforces a strict Zero Secret Exposure policy. API keys and credentials are automatically redacted server-side. Code is analyzed by a third-party AI provider under strict zero-retention terms, is not stored after analysis, is never executed, and is never used to train any model.
What is included in the 1 free rescan?
Every paid audit includes 1 rescan within 7 days. After applying the copy-paste coding-agent prompts in Cursor, Windsurf, or Replit to fix findings, users can request a rescan to verify fixes pass before going live.
What formats can I submit for private scans?
You can submit any public or private GitHub repository URL for analysis.
How does pricing work?
The tool offers simple transparent pricing: $0 for instant code snippet pre-scans, $5 for a full repository Launch Audit (one-time, includes 1 free rescan), and $39/month for Pro Builder Pass for active builders and teams.
Vibe Code Detector Website Engagement
Last Update: 9 days ago
Total Monthly Visits
0
Bounce Rate
0%
Visit Duration (avg)
0.00s
Pages Per Visit
0
Country Rank
0
United States
Global Rank
0
Monthly Traffic
Traffic Sources
Traffic Share By Country
- United States84.1%
- France15.1%
- Indonesia0.8%