OpenAI builds and deploys advanced AI models like GPT-4o for autonomous agents and workflows.
CleanSlop
$20/moStarting price
0Popularity
About CleanSlop
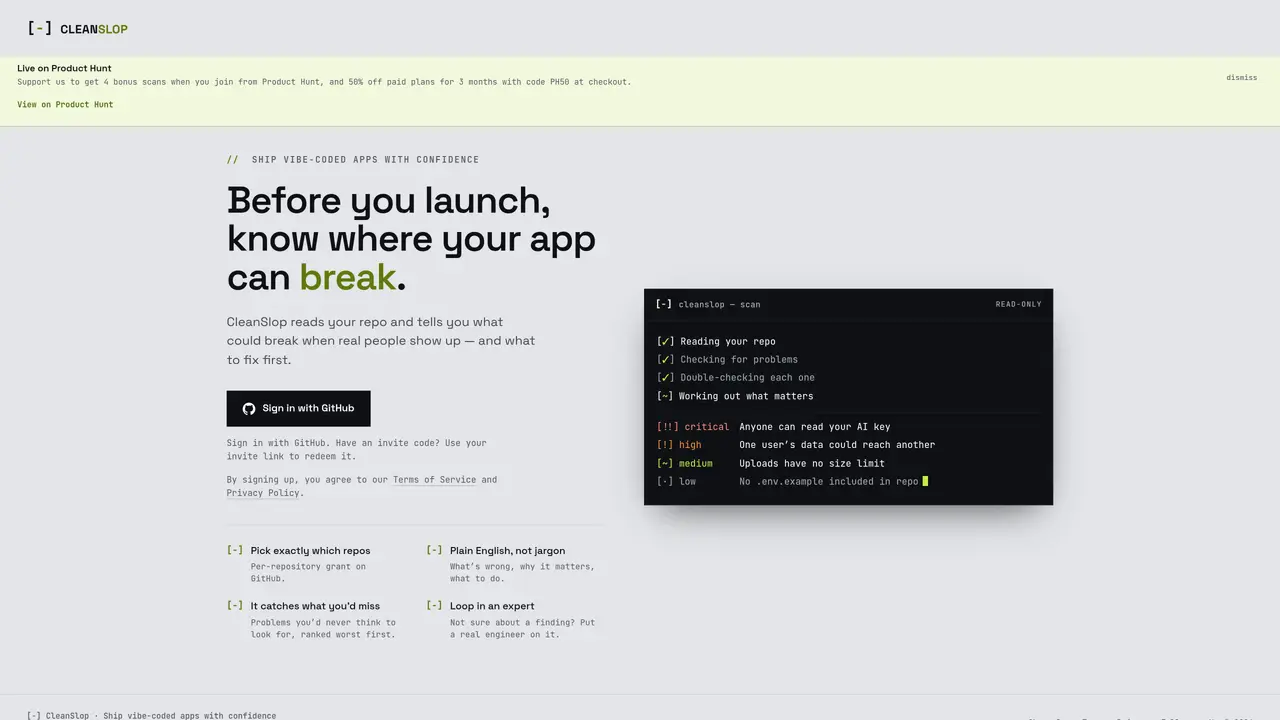
CleanSlop analyzes application repositories to identify potential failure points before deployment. It scans codebases to detect issues that could surface under real-world usage, ranking problems by severity so teams can prioritize fixes. The tool provides plain-language explanations of vulnerabilities, avoiding technical jargon to make findings accessible to all team members. Users can grant repository access via GitHub permissions, allowing CleanSlop to read code without modifying it. Findings are categorized by severity, with critical issues flagged for immediate attention. The service also offers expert consultation for ambiguous findings, connecting users with engineers to clarify technical risks.
Key features
- Repository scanning via GitHub permissions
- Severity-based issue ranking
- Plain-language vulnerability explanations
- Expert consultation for findings
- No file size limits on uploads
- Read-only repository access
- Critical issue prioritization
- Cross-platform compatibility
Use cases
- Pre-launch stability assessment for new applications
- Code review augmentation for engineering teams
- Risk identification in legacy codebases
Pros
- Reads repositories without modifying code
- Ranks issues by severity with plain-language explanations
- Provides expert consultation for ambiguous findings
- GitHub integration for repository access
- No size limits on file uploads
Cons
- Requires GitHub repository access for scanning
- No free tier or public pricing details
- Limited to static analysis of existing code
- No API documentation visible on homepage
Frequently asked questions about CleanSlop
What does CleanSlop do?
CleanSlop analyzes application repositories to identify potential failure points before deployment by scanning codebases for issues that could surface under real-world usage. It ranks problems by severity and provides plain-language explanations to make findings accessible to all team members.
Who is CleanSlop designed for?
CleanSlop is designed for development teams and individuals who want to proactively identify and address potential issues in their applications before deployment, ensuring more reliable and stable releases.
How does CleanSlop access my repository?
CleanSlop accesses repositories via GitHub permissions, allowing it to read code without making any modifications. Users can grant access on a per-repository basis.
Can CleanSlop help explain technical findings in simple terms?
Yes, CleanSlop provides plain-language explanations of vulnerabilities, avoiding technical jargon to ensure findings are understandable to all team members, regardless of their technical background.
Does CleanSlop offer support for ambiguous findings?
Yes, CleanSlop offers expert consultation for ambiguous findings, connecting users with engineers to clarify technical risks and provide additional guidance.
How do I get started with CleanSlop?
To get started, sign in with GitHub and grant CleanSlop access to the repositories you want to scan. The tool will then analyze the codebase and provide a report of potential issues.