OpenAI builds and deploys advanced AI models like GPT-4o for autonomous agents and workflows.
Execlave
$199Starting price
74Monthly visits
0Popularity
About Execlave
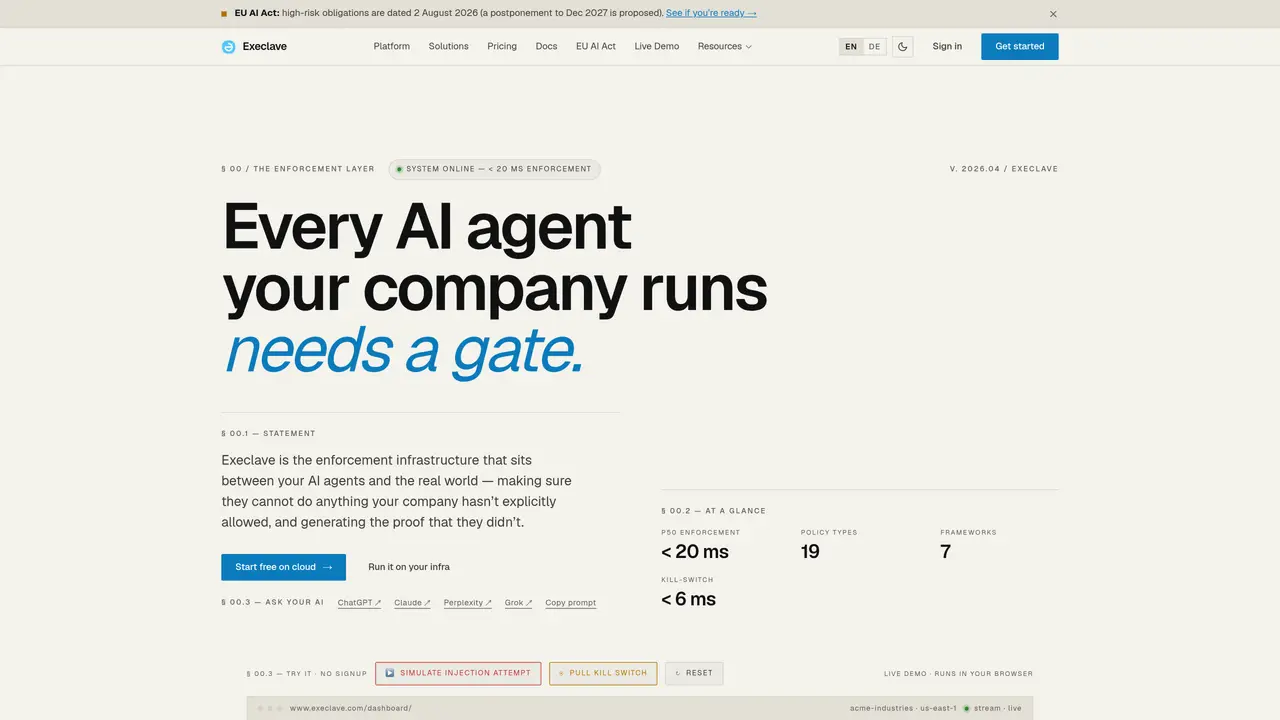
Execlave is a runtime enforcement layer positioned between AI agents and external systems to prevent unauthorized actions and generate cryptographically signed audit records. It intercepts every agent action, evaluates it against defined policies, and either allows, pauses for human review, or blocks the action in under 20 milliseconds. The platform provides real-time traces of agent activity with token-level precision, including input/output content, model metadata, token counts, latency, and cost tracking. Compliance reports are automatically generated for frameworks such as SOC 2, HIPAA, GDPR, ISO 27001, EU AI Act, PCI DSS, and NIST AI RMF. Execlave supports deployment both in the cloud and self-hosted environments, with SDKs available for TypeScript and Python to instrument agents in three lines of code. The system includes an emergency kill switch that can halt all agents server-side in under 6 milliseconds.
Key features
- Runtime policy enforcement
- Real-time agent traces with token-level precision
- Cryptographically signed audit logs
- Emergency kill switch (<6ms response)
- Automatic compliance reports (SOC 2, HIPAA, GDPR, etc.)
- TypeScript and Python SDKs
- Cloud and self-hosted deployment options
- Public API and webhooks
Use cases
- Governance of customer-facing AI agents in production
- Compliance auditing for regulated industries
- Prevention of prompt injection and data exfiltration
Pros
- Runtime policy enforcement with sub-20ms response time
- Automatic generation of compliance reports for multiple frameworks
- Real-time traces with token-level precision and audit logging
- Supports both cloud and self-hosted deployment options
- Emergency kill switch with sub-6ms server-side response
Cons
- Free plan limited to 1 agent and 500 traces per month
- Trace limits on paid plans may require overage fees
- No explicit support for mobile or edge deployment
- Self-hosted option starts at Starter plan
Frequently asked questions about Execlave
What does Execlave do?
Execlave acts as a runtime enforcement layer between AI agents and external systems, intercepting every action to evaluate it against defined policies before allowing, pausing, or blocking the action. It generates cryptographically signed audit records for compliance and real-time monitoring.
Who is Execlave designed for?
Execlave is designed for enterprises and teams deploying AI agents in production environments who require governance, compliance, and risk mitigation. It suits organizations needing to enforce policies, track agent activity, and generate audit reports for frameworks like SOC 2, HIPAA, or GDPR.
How does Execlave integrate with existing AI agents?
Execlave integrates with AI agents by adding a few lines of code using its TypeScript or Python SDKs. The SDK instruments agents to trace actions, enforce policies, and log activity without requiring changes to the underlying agent logic.
What compliance frameworks does Execlave support?
Execlave supports compliance frameworks including SOC 2, HIPAA, GDPR, ISO 27001, EU AI Act, PCI DSS, and NIST AI RMF. It automatically generates reports to help organizations meet audit and regulatory requirements.
Can Execlave be deployed in self-hosted environments?
Yes, Execlave supports deployment both in the cloud and self-hosted environments. Organizations can choose the deployment model that best fits their infrastructure and compliance needs.
What is the emergency kill switch in Execlave?
The emergency kill switch allows administrators to halt all AI agents server-side in under 6 milliseconds. This feature provides immediate control in case of policy violations or unexpected agent behavior, ensuring rapid response to risks.
Execlave Website Engagement
Last Update: 24 days ago
Total Monthly Visits
0
Bounce Rate
0%
Visit Duration (avg)
—
Pages Per Visit
0
Country Rank
—
Unknown
Global Rank
—