OpenAI builds and deploys advanced AI models like GPT-4o for autonomous agents and workflows.
Hakscan
$24/moStarting price
0Popularity
About Hakscan
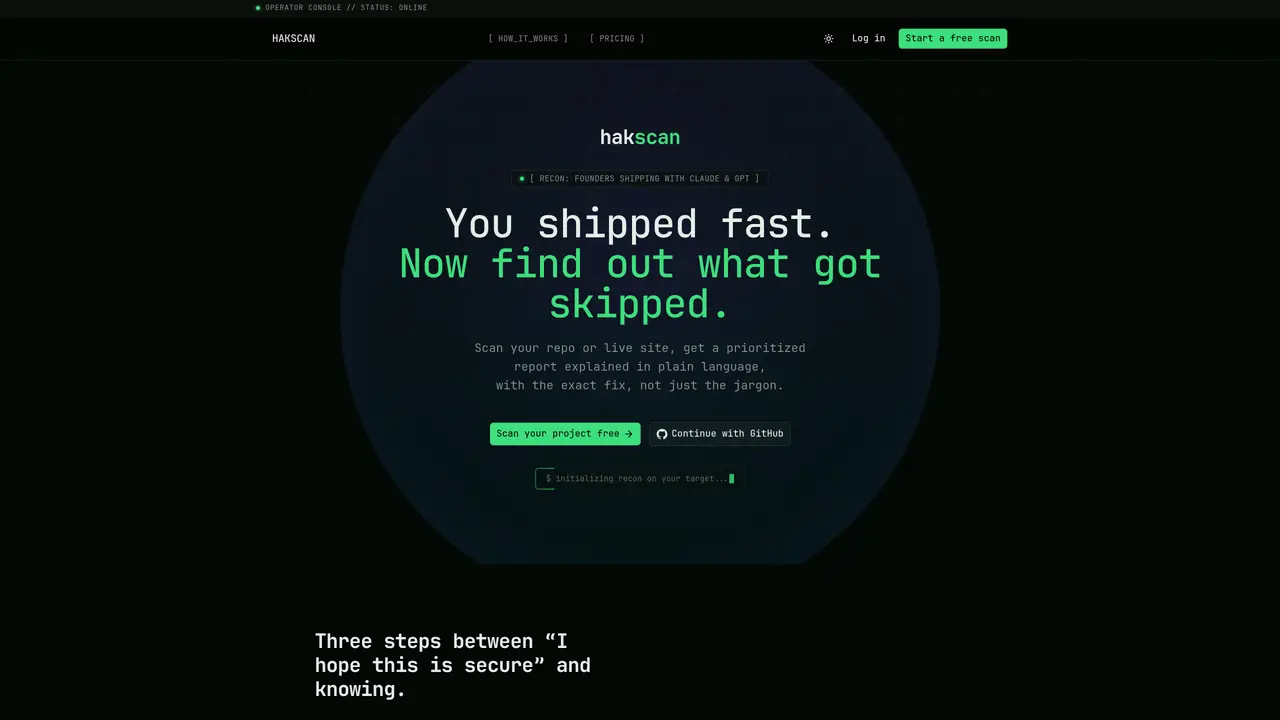
Hakscan is a security scanning tool designed to identify vulnerabilities in applications built with AI. It supports scanning both code repositories and live websites. Users must first prove ownership via GitHub OAuth, DNS record, or meta tag before any scan begins. The tool performs sandboxed scans using Semgrep and Gitleaks for repositories and a passive OWASP ZAP baseline for live sites, avoiding active exploitation. Raw findings are processed, deduplicated, and rewritten in plain language with business impact assessments and specific fix instructions. Reports are prioritized and can be generated manually or scheduled. The service offers a free tier with limited targets and manual scans, while the Pro plan includes unlimited targets, scheduled scans, priority queues, and PDF reports with email alerts.
Key features
- GitHub OAuth integration
- DNS record or meta tag verification
- Semgrep and Gitleaks for repository scanning
- Passive OWASP ZAP baseline for live sites
- AI-generated plain-language reports
- Business impact assessment in reports
- Manual and scheduled scan options
- PDF report generation
Use cases
- Identifying security flaws in AI-built applications
- Verifying security of newly deployed live websites
- Prioritizing and fixing vulnerabilities in code repositories
Pros
- Scans both repositories and live sites
- Uses multiple security tools (Semgrep, Gitleaks, OWASP ZAP)
- Provides plain-language explanations with actionable fixes
- No active exploitation during scans
- Ownership verification ensures targeted scanning
Cons
- Requires ownership attestation before every scan
- Free tier limited to one target
- No mention of multi-language support
- Pro plan required for advanced features
Frequently asked questions about Hakscan
What is Hakscan and what does it do?
Hakscan is a security scanning tool that identifies vulnerabilities in applications built with AI. It scans both code repositories and live websites to detect security flaws, providing prioritized reports with plain-language explanations, business impact assessments, and specific fix instructions.
Who should use Hakscan?
Hakscan is designed for developers and teams who have built AI applications and need to assess their security posture. It suits users who want to verify the security of their projects before deployment or identify overlooked vulnerabilities in existing systems.
How does Hakscan verify ownership of a project?
Users must prove ownership of a target before scanning begins. This can be done via GitHub OAuth for repositories or by verifying a live site through a DNS record or meta tag. No scan proceeds until ownership is confirmed.
What scanning methods does Hakscan use?
For repositories, Hakscan uses sandboxed scans with Semgrep and Gitleaks. For live websites, it employs a passive OWASP ZAP baseline scan, avoiding active exploitation. Raw findings are processed, deduplicated, and rewritten in plain language with actionable fixes.
What are the pricing options for Hakscan?
Hakscan offers a free tier with one target and manual scans, including basic reports. The Pro plan provides unlimited targets, scheduled scans, a priority scan queue, full PDF reports, and email alerts for a monthly fee.
How do I get started with Hakscan?
To get started, users can log in via GitHub OAuth, prove ownership of their target, and initiate a scan. The process involves three steps: proving ownership, running the sandboxed scan, and reviewing the AI-generated report with prioritized findings and fixes.