Frontier-grade Claude models with agentic workflows, strong coding, and enterprise guardrails delivered via developer console, web app, and cloud partners.

ShipSafe
0Popularity
About ShipSafe
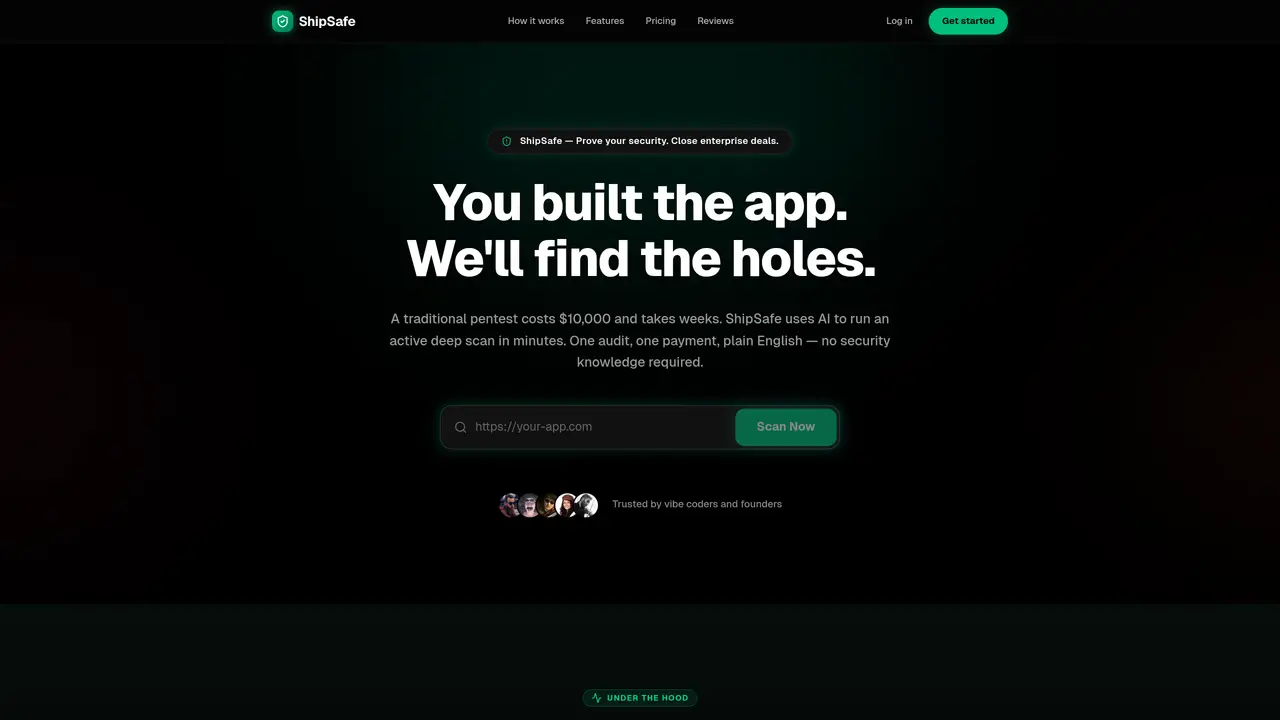
ShipSafe is an AI-powered security auditing tool that automates vulnerability scanning for web applications and APIs. It orchestrates industry-standard security tools such as ZAP, Nmap, Nikto, SSLyze, and Playwright to perform deep scans targeting the OWASP Top 10 vulnerabilities, infrastructure issues, and SSL/TLS configurations. The tool is designed for founders, developers, and AI app builders who lack specialized security expertise but need to demonstrate compliance, address vulnerabilities, and close enterprise deals without the cost or delay of traditional penetration testing. ShipSafe generates plain-English remediation reports that translate raw scan results into actionable fix steps, enabling users to understand and resolve security issues efficiently. It offers both a free Quick Scan for passive checks and a paid Deep Audit for full active exploit testing, with reports that can be shared directly with prospects, auditors, or compliance reviewers. The platform aims to simplify security assessments by providing a single dashboard, one-time pricing, and clear guidance tailored to non-technical users.
Key features
- AI-driven orchestration with Gemini 2.5 Pro
- Automated security scans using ZAP, Nmap, Nikto, SSLyze, and Playwright
- OWASP Top 10 deep audit generation
- Plain-English remediation reports
- Fast security assessments without penetration testing
- No requirement for specialized security expertise
- Enterprise compliance and deal-closing support
- Quick issue identification and resolution
Use cases
- Proving security compliance to enterprise clients
- Closing deals by demonstrating robust security practices
- Quickly identifying and fixing vulnerabilities without hiring security experts
Pros
- AI-driven orchestration with Gemini 2.5 Pro for automated security scanning
- Delivers plain-English remediation reports with step-by-step fixes
- Covers 38+ active exploit tests targeting OWASP Top 10 vulnerabilities
- One-time payment model with no subscription required
- Designed for non-technical founders and AI app builders
Cons
- Limited to web apps and APIs; does not cover on-premise infrastructure
- Deep Audit requires manual initiation and cannot be fully automated
- Report retention is 90 days for Quick Scan and permanent for Deep Audit
Frequently asked questions about ShipSafe
What exactly does ShipSafe do?
ShipSafe actively tests websites or APIs for over 38 vulnerabilities, including OWASP Top 10 issues, infrastructure weaknesses, and SSL/TLS misconfigurations. It uses AI to interpret scan results and generate plain-English reports with step-by-step remediation instructions.
Who is ShipSafe designed for?
The tool is built for founders, developers, and AI app builders who need to prove security without requiring specialized knowledge. It suits users who want to close enterprise deals, meet compliance requirements, or integrate security checks into their workflow.
How does ShipSafe pricing work?
ShipSafe offers a free Quick Scan for passive checks and a one-time paid Deep Audit for full active testing. There are no subscriptions or recurring fees; users pay only when they need an audit.
Does ShipSafe require domain verification?
No domain verification is required. Users can run a Quick Scan or Deep Audit on any URL immediately, as the process is fully automated without complex DNS configuration.
Can I integrate ShipSafe with other tools?
ShipSafe provides shareable report links and PDF exports, which can be integrated into workflows or shared with stakeholders. It does not currently offer direct API integrations with other security or development tools.
How do I get started with ShipSafe?
Users can start by running a free Quick Scan in minutes to identify exposed issues. For a comprehensive audit, they can upgrade to the Deep Audit, which performs active exploit testing and generates a detailed report with remediation steps.