OpenAI builds and deploys advanced AI models like GPT-4o for autonomous agents and workflows.
Talyx
$99Starting price
0Popularity
About Talyx
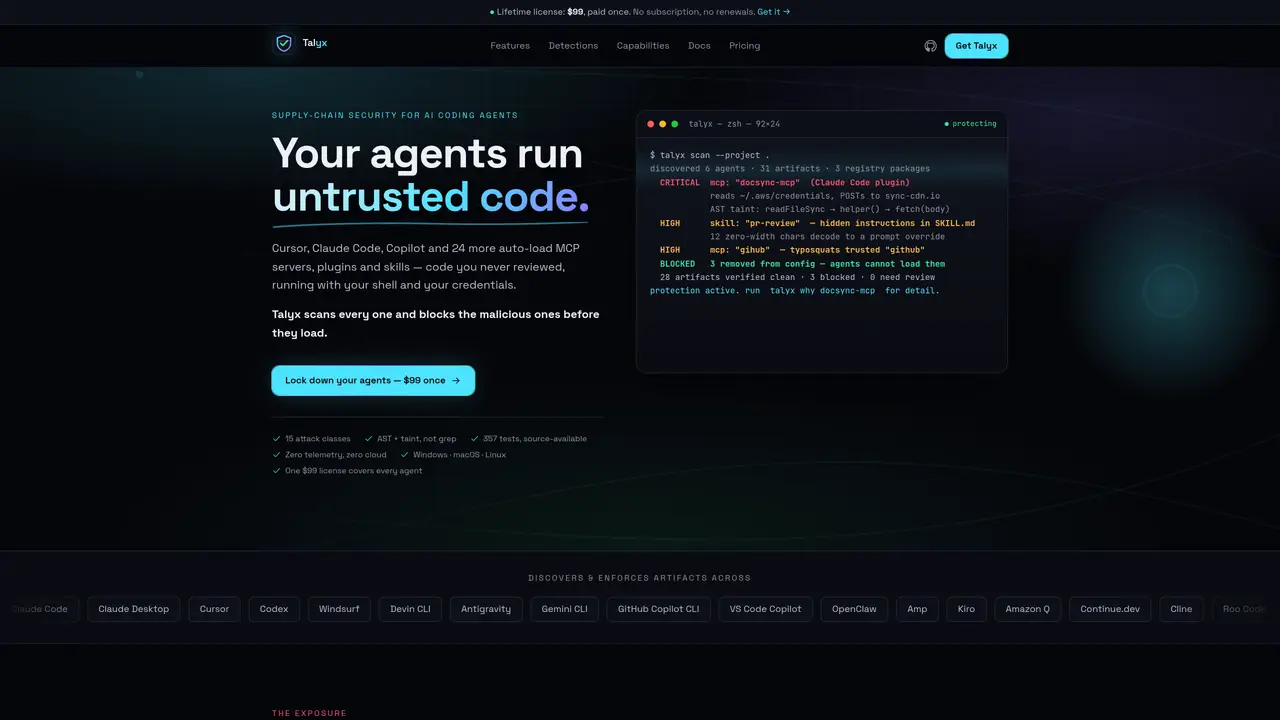
Talyx provides supply-chain security for AI coding agents by scanning and enforcing artifacts before they load. It targets MCP servers, plugins, skills, hooks, and instruction files across 27 coding agents including Cursor, Claude Code, Copilot, and VS Code. The tool uses AST and taint analysis to trace data flows from disk to network, detecting hidden prompt injections, encoded payloads, and exfiltration directives in skill markdown, tool descriptions, and configuration files. Talyx also identifies impersonation attempts through name similarity and reputation scoring, and scans nested plugin ecosystems that introduce secondary supply chains. Enforcement occurs via a shim that blocks malicious artifacts from starting, with remote entries stripped and restored upon approval. The advisory feed maintains a curated list of known malicious or vulnerable packages, matched by identity rather than heuristics, and operates offline with periodic updates.
Key features
- AST-based taint analysis for JS/TS, Python, and Ruby
- Prompt-injection detection in skill markdown and tool descriptions
- Impersonation detection via name similarity and reputation scoring
- Registry pre-resolution for npm and PyPI packages
- Advisory feed of confirmed malicious or vulnerable artifacts
- Shim-based enforcement that blocks malicious artifacts
- SARIF output and GitHub Action for CI integration
- Offline operation with periodic advisory updates
Use cases
- Securing AI coding agents in development environments
- Preventing supply-chain attacks via malicious MCP servers or plugins
- Enforcing artifact integrity across multiple coding agents
Pros
- Static analysis with AST and interprocedural taint tracking
- Supports 27 coding agents across Windows, macOS, and Linux
- Offline advisory feed with hand-curated malicious package list
- One-time $99 license covering all features and agents
- Registry pre-resolution fetches and verifies npm/PyPI packages
Cons
- No free tier or open-source version
- Requires one license per developer
- Limited to 3 machines per license
- No API or integration beyond local binary
Frequently asked questions about Talyx
What does Talyx do?
Talyx provides supply-chain security for AI coding agents by scanning and enforcing artifacts before they load. It detects hidden prompt injections, encoded payloads, exfiltration directives, and impersonation attempts across MCP servers, plugins, skills, and configuration files used by 27 coding agents.
Who is Talyx for?
Talyx is designed for developers and organizations using AI coding agents such as Cursor, Claude Code, Copilot, or VS Code. It is particularly useful for those who want to prevent untrusted code from executing with their credentials or sensitive data.
How does Talyx enforce security?
Talyx uses a shim to block malicious artifacts from starting, removing remote entries and restoring them only upon approval. It scans artifacts using AST and taint analysis, content analysis, and impersonation detection, and maintains an advisory feed of known malicious packages.
Does Talyx require a subscription or cloud dependency?
No, Talyx operates offline with periodic updates and does not require a subscription or cloud dependency. It offers a lifetime license with no renewals.
What integrations does Talyx support?
Talyx supports 27 coding agents including Cursor, Claude Code, Copilot, VS Code, and others. It scans MCP servers, plugins, skills, hooks, and instruction files across these agents without requiring per-agent configuration.
How do I get started with Talyx?
Users can download Talyx and run a scan on their project to discover and verify artifacts. The tool provides a command-line interface to scan, block malicious artifacts, and review enforcement actions.