OpenAI builds and deploys advanced AI models like GPT-4o for autonomous agents and workflows.
Anvilogic
$1Starting price
4.7KMonthly visits
11Popularity
About Anvilogic
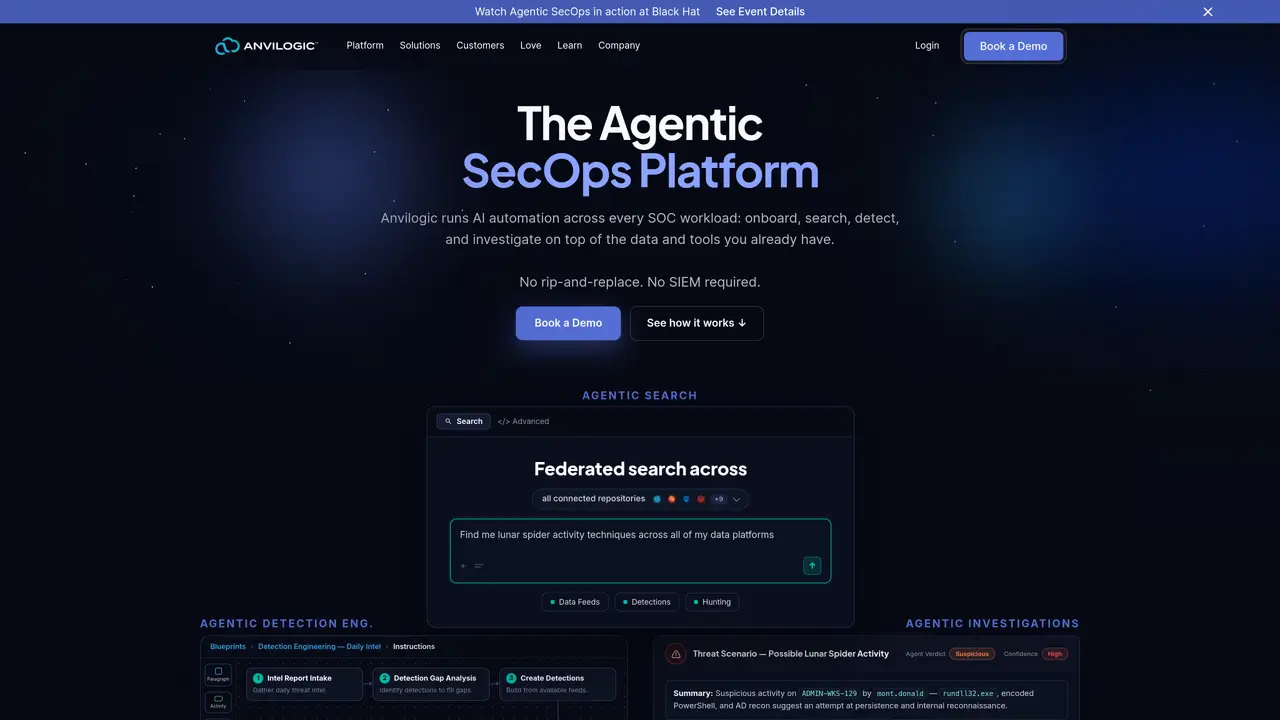
Anvilogic is a cutting-edge cybersecurity platform designed to revolutionize the way enterprises handle threat detection and response. As someone who has navigated the complexities of cybersecurity solutions, I appreciate Anvilogic’s approach to breaking free from traditional SIEM (Security Information and Event Management) constraints. The platform offers a multi-data platform SIEM that integrates seamlessly with existing data lakes like Splunk, Azure, and Snowflake, allowing users to manage security data without the need to replace their current systems. Key Features: Multi-Data Platform Coverage: Anvilogic supports threat detection across various SIEM and data lake environments, providing flexibility in data management. Custom Detection Builder: Utilizes an AI-assisted interface to help users create and deploy detection logic effortlessly, even without deep coding knowledge. Threat Detection Library: Access to thousands of pre-built detection rules and scenarios, continuously updated to address new threats. Multi-Cloud Threat Detection: Offers robust, out-of-the-box cloud-native threat coverage, ensuring comprehensive security across all environments. Anvilogic is suitable for large enterprises, Security Operations Centers (SOCs), financial services, healthcare institutions, and educational institutions. It can be used for uncommon use cases such as training cybersecurity students and cost-effective security management by non-profits. The pricing model is custom-based, tailored to the specific needs and scale of an organization.
Key features
- Multi-data platform coverage
- Custom detection builder with AI-assisted interface
- Threat detection library with thousands of pre-built rules
- Multi-cloud threat detection
- Cost efficiency by reducing SIEM licensing costs
- Time savings through efficient detection rule building and deployment
- Enhanced threat coverage with extensive libraries and multi-cloud capabilities
Use cases
- Large enterprises implementing sophisticated threat detection and response strategies
- Security Operations Centers (SOCs) enhancing their operational efficiency and detection capabilities
- Financial services protecting sensitive data with robust, scalable threat detection systems
Pros
- Eliminates the need for SIEM replacement or data migration, operating on top of existing infrastructure
- Supports federated search across multiple SIEMs, data lakes, and storage services without data movement
- Provides AI-powered agents for automating SOC workflows such as onboarding, detection engineering, and investigation
- Offers pre-built blueprints to streamline end-to-end security automation
- Designed by practitioners with hands-on SOC experience, ensuring practical usability
Cons
- May require initial setup and configuration to align with existing security tools and workflows
- Dependent on the capabilities and limitations of connected third-party platforms
Frequently asked questions about Anvilogic
What is Anvilogic and what does it do?
Anvilogic is an AI-powered Agentic SecOps platform designed to automate security operations across every SOC workload, including onboarding, search, detection, and investigation. It operates on top of existing data and tools without requiring migration or replacement of current systems.
Who is Anvilogic suitable for?
Anvilogic is suitable for large enterprises, Security Operations Centers (SOCs), financial services, healthcare institutions, educational institutions, and organizations looking to modernize their security operations with AI-driven automation.
How does Anvilogic integrate with existing systems?
Anvilogic integrates with a wide range of SIEMs, data lakes, and storage services, including Splunk, Azure Sentinel, Snowflake, Databricks, Amazon S3, and Google Cloud Storage. It connects via connectors and APIs without requiring data to be moved.
What are the key capabilities of Anvilogic?
Key capabilities include AI-driven agents for onboarding, searching, detecting, and investigating security threats, as well as blueprints for automating end-to-end security workflows. It also supports custom detection engineering and a library of pre-built detection rules.
Does Anvilogic require a SIEM to function?
No, Anvilogic does not require a SIEM to function. It operates on top of existing data lakes, storage services, or SIEMs, providing flexibility to work with the tools already in place.
How can I get started with Anvilogic?
Prospective users can book a demo or contact Anvilogic to explore how the platform can be tailored to their specific security operations needs. The platform is designed to be deployed alongside existing systems with minimal disruption.
Anvilogic Website Engagement
Last Update: 9 days ago
Total Monthly Visits
0
Bounce Rate
0%
Visit Duration (avg)
0.00s
Pages Per Visit
0
Country Rank
0
United States
Global Rank
0
Category Rank
#0
Computer Security
Monthly Traffic
Traffic Sources
Traffic Share By Country
- United States58.1%
- India37.3%
- Turkey4.6%