Generate captions, optimize content, and enhance with custom images for maximum engagement.
46M visits/mo-10%#3 Image & Design
Revolutionize cybersecurity with this AI-driven, rapid, accurate pentesting tool.
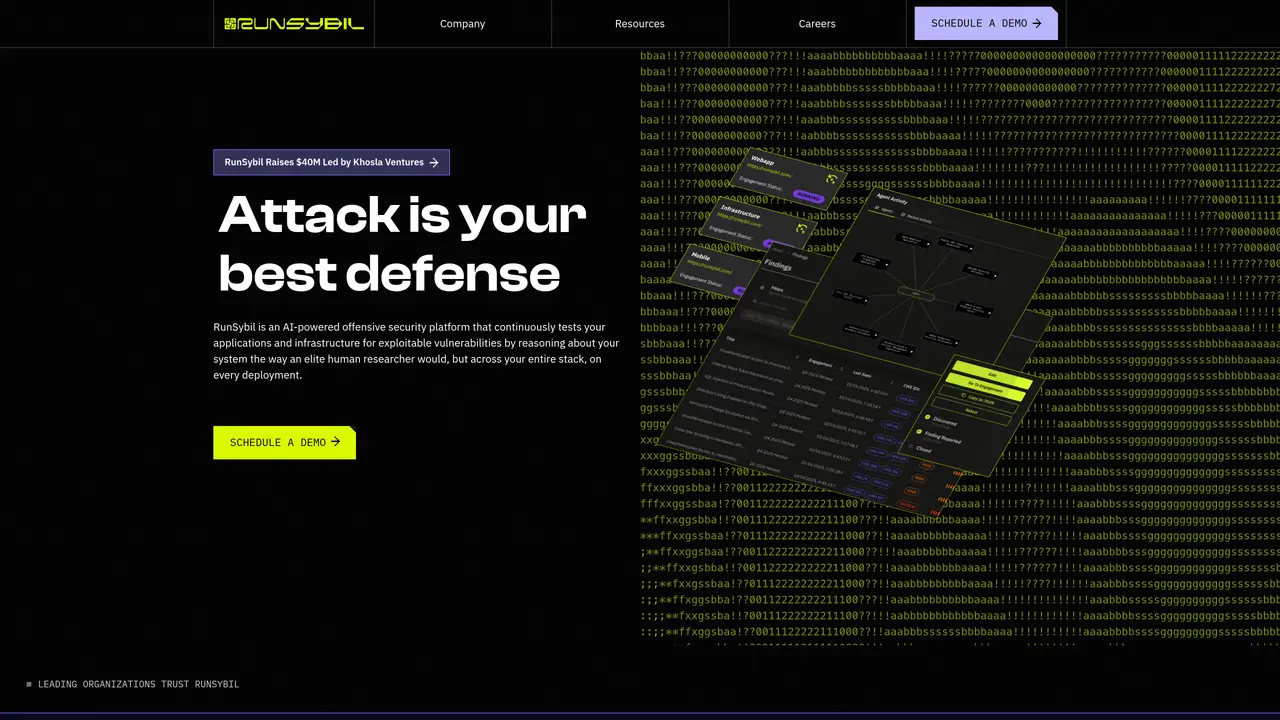
RunSybil is an advanced AI-driven pentesting tool designed to transform the cybersecurity landscape by automating hacker intuition. It helps organizations of all sizes identify and address vulnerabilities swiftly and accurately. By reducing the time and cost associated with vulnerability discovery, RunSybil offers a proactive approach to protecting digital assets from potential threats. The tool uses sophisticated AI algorithms to simulate advanced cyber-attacks, identifying vulnerabilities with high precision. It also provides real-time insights into pentest findings, moving away from traditional delayed report formats. Additionally, RunSybil supports re-testing of security patches or fixes to ensure vulnerabilities are effectively addressed. This makes it an essential tool for proactive security management. RunSybil is suitable for tech startups, financial institutions, healthcare providers, educational institutions, and non-profits securing donor information. The tool offers a free tier with limited access to its features at no cost, while the Pro Tier provides comprehensive security solutions starting at $99 per month.
RunSybil is an AI-powered offensive security platform that continuously tests applications and infrastructure for exploitable vulnerabilities by reasoning about systems the way an elite human researcher would. It evaluates changes with every deployment, identifies attack paths, and validates exploitability rather than relying on periodic scans or signature-based detection.
RunSybil is designed for organizations that require continuous, proactive security testing, including tech startups, financial institutions, healthcare providers, and enterprises managing critical systems. It suits teams that need real-time insights and measurable improvements in security posture.
Unlike traditional pentests that provide delayed reports after a fixed engagement, RunSybil offers continuous testing with feedback on every pull request. It reasons across the entire stack—code, APIs, cloud, and infrastructure—to find vulnerabilities missed by generic scanners and validates exploitability in real time.
Yes, RunSybil integrates into development workflows by providing security feedback at the commit stage, ensuring vulnerabilities are caught early. It supports CI/CD pipelines and aligns with engineering cadence to reduce the time between detection and remediation.
RunSybil detects a wide range of vulnerabilities, including logic flaws, business logic issues like cross-tenant data access, IAM misconfigurations, container escapes, CI/CD secret exposure, and lateral movement paths. It chains vulnerabilities across layers to identify real, exploitable attack paths.
Prospective users can schedule a demo or request a sample report through the RunSybil website. The platform offers a free tier with limited access, while the Pro Tier provides comprehensive security solutions. Organizations can also contact the team for tailored onboarding.
runsybil.com · third-party estimates from Similarweb
Last 4 months · grows by one month every month
Share of visits · estimated visits
Automation & Agents · Sep 2026
Traffic figures are third-party estimates, good for scale and trends; they can differ from a company's own numbers. Updated monthly.
We use essential cookies to run aitoolnavio™, and optional cookies to analyze traffic and measure our marketing. You choose what we use — optional cookies stay off unless you turn them on. See our Privacy Policy.
One short email a week: fresh tools worth trying, honest takes and the updates that actually matter. No spam, unsubscribe any time.
Generate captions, optimize content, and enhance with custom images for maximum engagement.
Build conversational forms, capture rich responses, and automate follow-ups with AI-powered surveys and workflows.
Automate code, research, and documents using agents.
AI-powered IDE for autonomous coding tasks and agentic development workflows
Source, match, and manage talent with predictive analytics for effortless recruiting.
Automate workflow, optimize operations, and detect potential issues with this efficient AI-driven solution.
Transforms thoughts into actions, enhancing productivity and efficiency.
AI Recruitment engine to hire top global talent
All-in-one team productivity platform combining chat, docs, video meetings, workflows, and AI tools in one place.
Personal assistant that coordinates tasks across apps and devices via text or call
AI automation and agent-building platform with 3,000+ app integrations
AI job search copilot that matches roles to skills, optimizes resumes for ATS, generates cover letters, and autofills applications with real-time insights.
Matched on what this tool does — grouped by the job you would be replacing.
matches AI-driven pentesting · Rapid onboarding · Attack replay
Automate cybersecurity, enhance code security, integrate seamlessly with SAST tools.
Continuous autonomous AI pentesting for applications, APIs and infrastructure
AI security scanning platform that detects exploitable vulnerabilities in code, logic, and infrastructure and delivers fixes via PRs and CI/CD pipelines.
matches AI-driven pentesting · Efficiency in detection · Enhanced security posture
Unified cloud security platform that maps risks across cloud, code, runtime, identities, and AI workloads with graph-based prioritization and code-to-cloud remediation.
AI-driven API security platform that discovers APIs, detects threats, and protects against attacks in real time.