OpenAI builds and deploys advanced AI models like GPT-4o for autonomous agents and workflows.
CodeAnt AI
$20Starting price
86KMonthly visits
32Popularity
About CodeAnt AI
CodeAnt AI is an AI-driven code health platform designed for engineering teams, consolidating code review, security scanning, quality analysis, and developer productivity metrics into a single system. It operates across pull requests and full codebases, providing real-time feedback and insights to improve code quality and security. The platform includes AI-powered code reviews with inline comments, instant pull request summaries, and one-click fix suggestions for bugs, vulnerabilities, and quality issues. Security features encompass SAST, secret detection, SCA, and IaC scanning for Terraform, Kubernetes, and cloud configurations. Code quality analysis covers maintainability, duplication, complexity, style enforcement, quality gates, and test coverage signals. Developer metrics track DORA indicators such as lead time, deployment frequency, mean time to recovery, PR sizes, and hotspots. CodeAnt AI integrates with IDEs, CI/CD pipelines, and Git platforms including GitHub, GitLab (cloud and self-hosted), Bitbucket, and Azure DevOps, supporting over 30 programming languages and monorepos. It offers a proprietary AST + LLM engine for context-aware analysis of code intent and data flow, with a self-hosted option available for enhanced security. The platform is recognized as a Y Combinator company and listed as a Code Review Assistant in the Atlassian ecosystem.
Key features
- AI-powered code reviews with inline feedback and one-click fixes
- Security scanning including SAST, secret detection, SCA, and IaC scanning
- Code quality analysis for maintainability, duplication, complexity, and style enforcement
- Developer productivity metrics tracking (DORA indicators)
- Integration with IDEs, CI/CD pipelines, and Git platforms (GitHub, GitLab, Bitbucket, Azure DevOps)
- Support for 30+ programming languages and monorepos
- Proprietary AST + LLM engine for context-aware code analysis
- Self-hosted deployment option for security-conscious organizations
- Instant pull request summaries and vulnerability detection
Use cases
- Monitoring and mitigating security threats in code repositories
- Writing and maintaining high-quality, maintainable code
- Documenting code changes and generating pull request summaries
Pros
- Autonomous agentic security that maps attack surfaces and chains real exploits to verify vulnerabilities
- Continuous penetration testing that auto-retests assets on every deployment for real-time coverage
- Context-aware analysis combining code, infrastructure, and runtime data to identify exploitable paths
- Provides verified exploit reports with reproduction steps and impact assessment
- Supports cloud threat detection and dynamic application security testing (DAST) for running apps and APIs
Cons
- Focused primarily on security rather than broader code quality or developer productivity metrics
- May require significant setup and configuration for full integration into existing workflows
- Agentic approach could generate a high volume of findings, requiring prioritization and review effort
Frequently asked questions about CodeAnt AI
What does CodeAnt AI do?
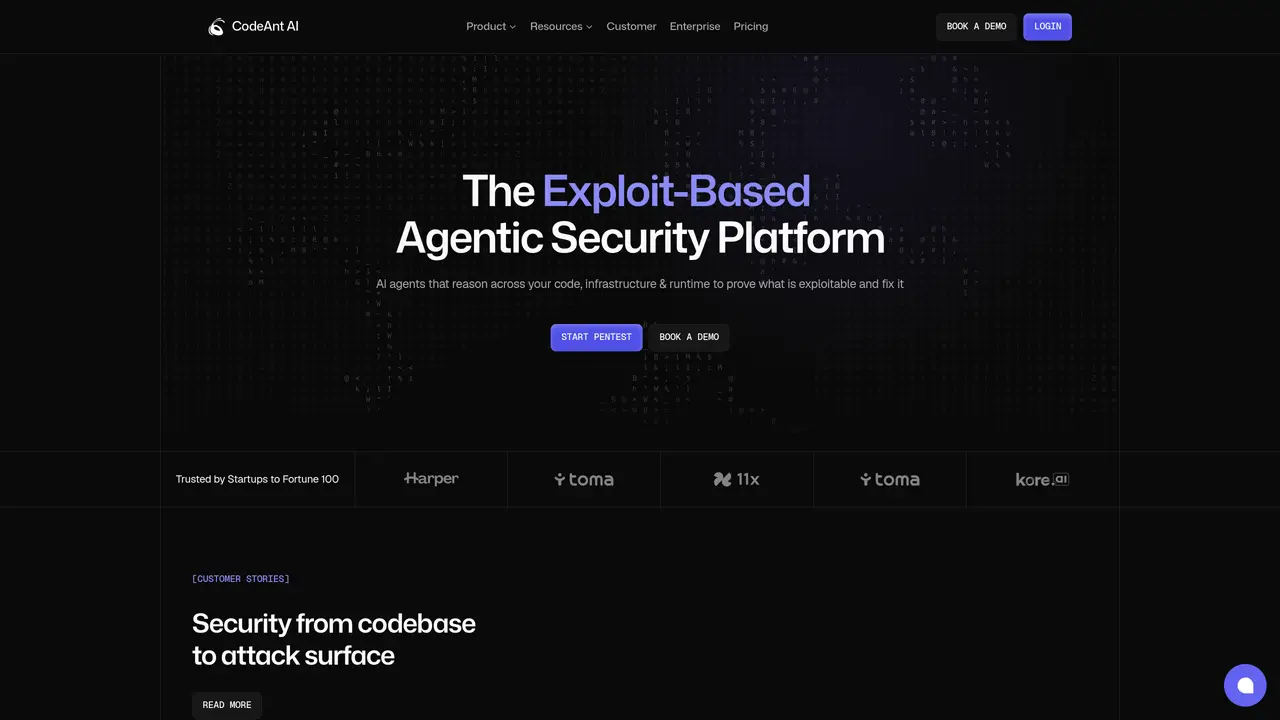
CodeAnt AI is an agentic security platform that uses autonomous agents to map attack surfaces, chain real exploits, and verify vulnerabilities in code, infrastructure, and runtime environments. It provides continuous pentesting by automatically retesting assets on every deployment.
Who should use CodeAnt AI?
The platform is designed for engineering and security teams, including startups and Fortune 100 companies, who need to identify and remediate exploitable vulnerabilities across their entire technology stack.
How does CodeAnt AI integrate with existing workflows?
CodeAnt AI integrates with CI/CD pipelines and development workflows to run security checks before code merges, providing real-time feedback and prioritizing findings based on actual exposure rather than raw CVSS scores.
Does CodeAnt AI support self-hosting?
Yes, CodeAnt AI offers a self-hosted option for enhanced security and compliance, allowing organizations to deploy the platform within their own infrastructure.
What types of security testing does CodeAnt AI perform?
CodeAnt AI performs static analysis (SAST), dynamic application security testing (DAST), infrastructure scanning (CSPM), dependency vulnerability scanning, and secret detection, all while simulating real-world attack paths.
How do I get started with CodeAnt AI?
Prospective users can start by booking a demo or signing up for a trial on the CodeAnt AI website. The platform is designed to be deployed quickly and can begin scanning codebases and infrastructure immediately.
CodeAnt AI Website Engagement
Last Update: 9 days ago
Total Monthly Visits
0
Bounce Rate
0%
Visit Duration (avg)
0.00s
Pages Per Visit
0
Country Rank
0
India
Global Rank
0
Category Rank
#0
Graphics Multimedia & Web Design
Monthly Traffic
Traffic Sources
Traffic Share By Country
- India41.7%
- United States13.4%
- Brazil3.8%
- Russia2.8%
- Germany2.6%