OpenAI builds and deploys advanced AI models like GPT-4o for autonomous agents and workflows.

Snyk
$1Starting price
850KMonthly visits
49Popularity
About Snyk
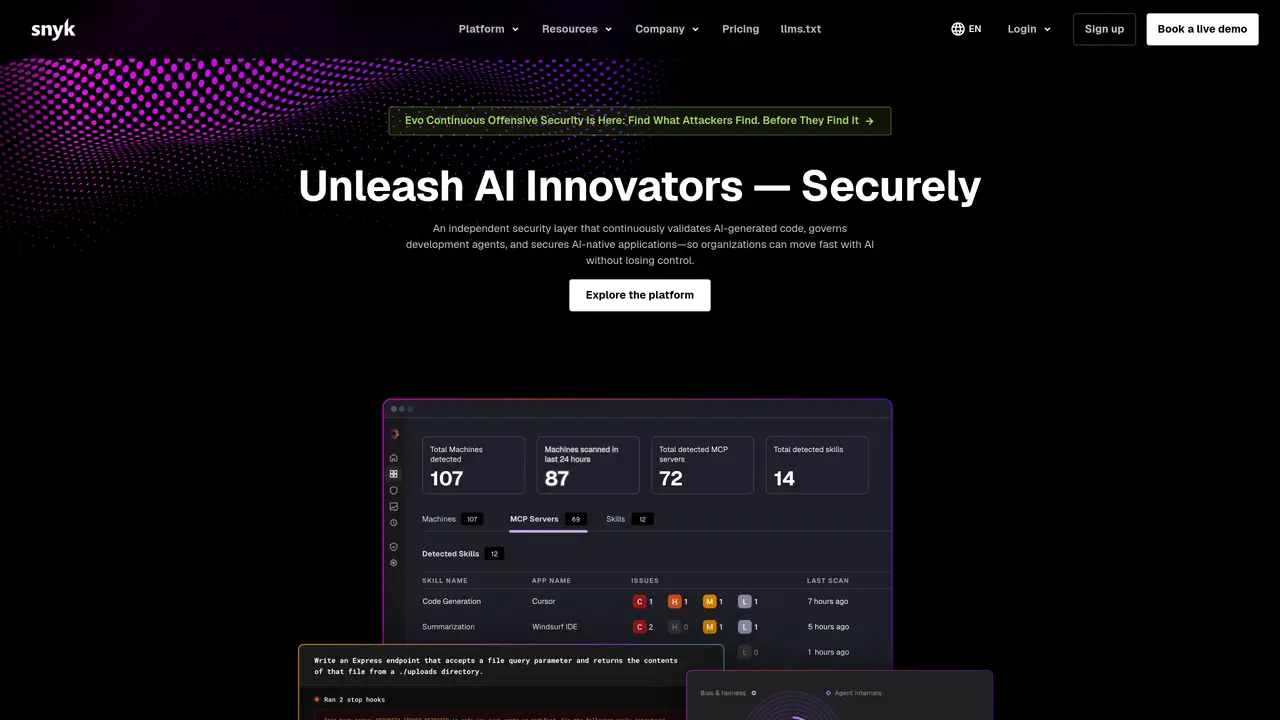
Snyk is a code analysis tool that helps developers identify and fix vulnerabilities in their code. It uses a combination of static analysis, dependency scanning, and container security to provide a comprehensive view of security risks. Snyk is easy to use and implement, with a user-friendly interface and detailed reporting system. It is effective at finding vulnerabilities in code and monitoring for security mistakes in dependencies. Snyk is suitable for developers, DevOps teams, and organizations of all sizes. It is compatible with a wide range of systems, including cloud environments, container environments, and popular programming languages. Snyk’s real-time monitoring capabilities ensure that new vulnerabilities are identified as soon as they are introduced. Snyk has received positive feedback from users who appreciate its user-friendly interface, detailed reporting system, and effective vulnerability detection capabilities. However, some users have pointed out that the pricing may not be suitable for medium-sized businesses, and that certain languages or frameworks are not supported. Snyk is known for its high performance and accuracy in identifying security risks in code. It is a valuable tool for any organization that wants to ensure the security of its code and prevent vulnerabilities from being introduced into its systems.
Snyk
Boston · Founded 2015
- Founded
- 2015
- Headquarters
- Boston
Key features
- Easy to use and implement
- Comprehensive reporting structure with remediation suggestions
- Integrations with management tools
- Effective at finding vulnerabilities in code
- Monitoring for security mistakes in dependencies
- Real-time monitoring capabilities
- Support for a wide range of systems
- High performance and accuracy in identifying security risks
Use cases
- Identifying and fixing vulnerabilities in third-party libraries and dependencies
- Securing container environments and identifying potential security risks
- Scanning IaC templates to identify security risks in cloud infrastructure
Pros
- Integrates security into existing development workflows through IDEs, CI/CD pipelines, and AI coding assistants
- Provides continuous monitoring and real-time alerts for vulnerabilities in code, dependencies, and AI-generated content
- Supports multiple security domains including code, open-source dependencies, containers, infrastructure as code, and AI-native applications
- Offers risk-based prioritization to focus on the most critical vulnerabilities first
- Includes detailed reporting and remediation guidance for identified security issues
Cons
- May require configuration to align with specific organizational security policies and workflows
- Certain advanced features or integrations may have a learning curve for teams unfamiliar with security tools
Frequently asked questions about Snyk
What does Snyk do?
Snyk is an AI security platform that secures code written by AI, the agents it runs, and the applications it builds from inception to production. It helps organizations identify and mitigate vulnerabilities in AI-generated code, dependency chains, containers, infrastructure as code, and APIs.
Who is Snyk suitable for?
Snyk is designed for AI teams, developers, DevOps engineers, and security professionals who need to secure AI-native applications, agentic workflows, and traditional software supply chains. It is used by organizations of various sizes, from startups to large enterprises.
How does Snyk integrate with existing tools?
Snyk integrates with popular development environments, CI/CD pipelines, and AI coding assistants such as IDEs, Git platforms, and tools like Claude Code, Cursor, and Codex. It provides a unified security layer across the entire software development lifecycle.
What types of vulnerabilities does Snyk detect?
Snyk detects vulnerabilities in AI-generated code, open-source dependencies, container images, infrastructure configurations, secrets exposure, and API endpoints. It also identifies risks introduced by agentic development workflows and AI-native applications.
How does Snyk prioritize security risks?
Snyk uses risk-based prioritization to help teams focus on the most critical vulnerabilities first. It provides contextual insights, such as exploitability and potential impact, to streamline remediation efforts and reduce exposure to threats.
How can I get started with Snyk?
Users can start with Snyk by creating a free account on the platform, which allows them to scan code repositories, dependencies, and containers. The platform offers guided onboarding and documentation to help teams integrate Snyk into their workflows quickly.
Snyk Website Engagement
Last Update: 9 days ago
Total Monthly Visits
0
Bounce Rate
0%
Visit Duration (avg)
0.00s
Pages Per Visit
0
Country Rank
0
United States
Global Rank
0
Category Rank
#0
Programming & Developer Software
Monthly Traffic
Traffic Sources
Traffic Share By Country
- United States29.5%
- India8.1%
- United Kingdom6.7%
- Germany5.3%
- Vietnam3.5%