Open-source platform combining product analytics, session replay, A/B testing, and feature flags in one toolkit for product engineers.

SonarQube
FreeStarting price
918Monthly visits
0Popularity
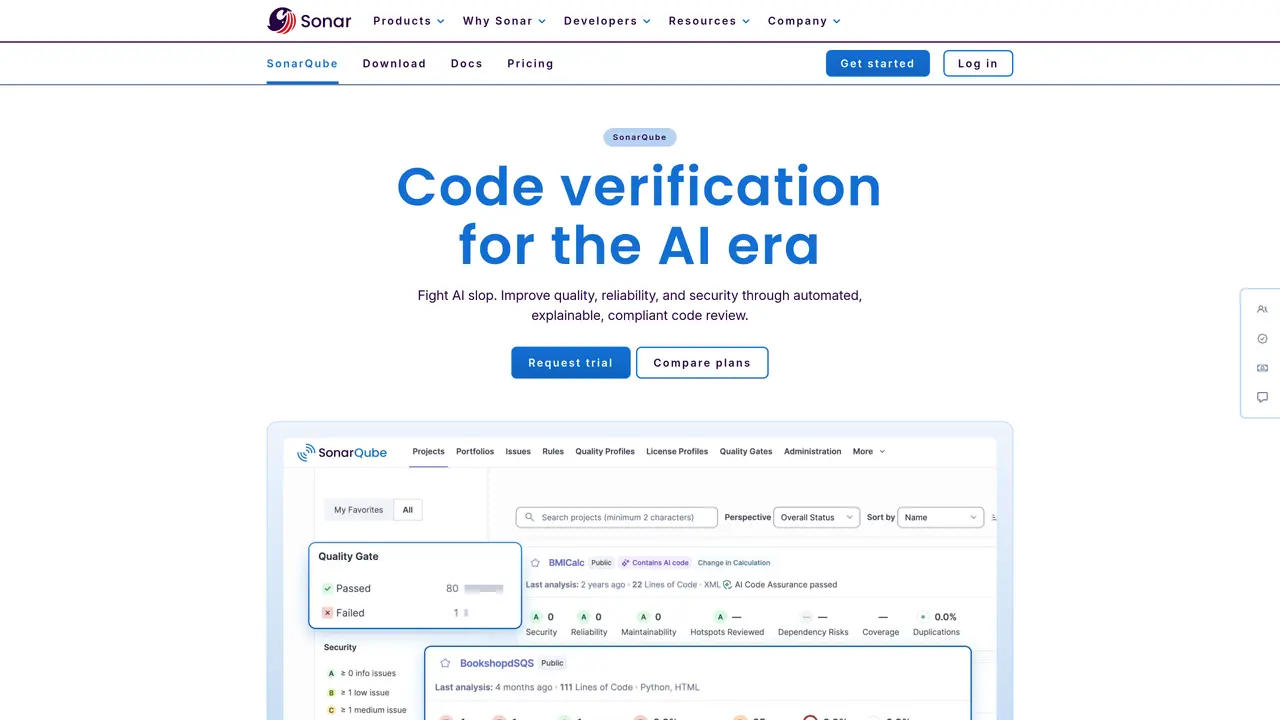
About SonarQube
SonarQube is an advanced code analysis tool designed to help software development teams improve the quality of their code. It can scan source code for various errors and vulnerabilities, and generate comprehensive reports that provide insight into the quality of the code. SonarQube also offers automated code review and feedback, which can be used to identify potential issues and areas of improvement. Additionally, it offers a suite of powerful plug-ins to extend its functionality, allowing teams to customize their code analysis to meet their unique needs. With SonarQube, teams can ensure that their code is up to the highest standards of quality, giving them peace of mind when releasing their software to the public. It can be used for various tasks such as identifying potential errors and vulnerabilities in code, automating code review and feedback, and customizing code analysis to meet team needs.
Key features
- Identify potential errors and vulnerabilities in code
- Automate code review and feedback
- Customize code analysis to meet team needs
- Generate comprehensive reports on code quality
- Offer automated code review and feedback
- Provide a suite of powerful plug-ins for customization
Use cases
- Identifying potential errors and vulnerabilities in code
- Automating code review and feedback processes
- Customizing code analysis to meet team needs and improve code quality
Pros
- Static code analysis for over 40 programming languages and frameworks
- Integrates with CI/CD pipelines and version control systems like GitHub, Bitbucket, and Azure DevOps
- Provides automated code review and real-time feedback within IDEs
- Offers advanced security features including SAST, SCA, and secrets detection
- Supports both cloud-based and self-managed deployment options
Cons
- May require significant setup and configuration for optimal use
- Some advanced features are only available in higher-tier plans
- Can produce a large volume of alerts that require triage and prioritization
Frequently asked questions about SonarQube
What is SonarQube and what does it do?
SonarQube is a static code analysis tool that inspects source code for bugs, vulnerabilities, and code smells, providing continuous feedback to improve code quality and security throughout the development lifecycle.
Who should use SonarQube?
SonarQube is designed for developers, security teams, platform engineers, and organizations focused on maintaining high code quality, security standards, and compliance across various programming languages and frameworks.
How does SonarQube integrate with development workflows?
SonarQube integrates with CI/CD pipelines, IDEs, and version control systems like GitHub, Bitbucket, Azure DevOps, and GitLab to provide automated code analysis and real-time feedback during development and deployment.
What are the deployment options for SonarQube?
SonarQube offers both cloud-based (SonarQube Cloud) and self-managed (SonarQube Server) deployment options, along with a free IDE extension for on-the-fly analysis and coding guidance.
Does SonarQube support AI-generated code validation?
Yes, SonarQube includes features to validate AI-generated code for security and quality, ensuring that code produced by LLMs meets organizational standards before deployment.
What languages and frameworks does SonarQube support?
SonarQube supports over 40 programming languages and frameworks, including Java, JavaScript, Python, C#, and more, enabling broad compatibility across diverse tech stacks.
SonarQube Website Engagement
Last Update: 1 month ago
Total Monthly Visits
0
Bounce Rate
0%
Visit Duration (avg)
—
Pages Per Visit
0
Country Rank
—
Unknown
Global Rank
—