Privacy-focused AI chatbot that generates uncensored text, code, images, and translations without storing conversations or requiring an account.
20M visits/mo+18.6%#13 Coding & Development
AI-assisted static analysis and application security posture management with evidence tracking
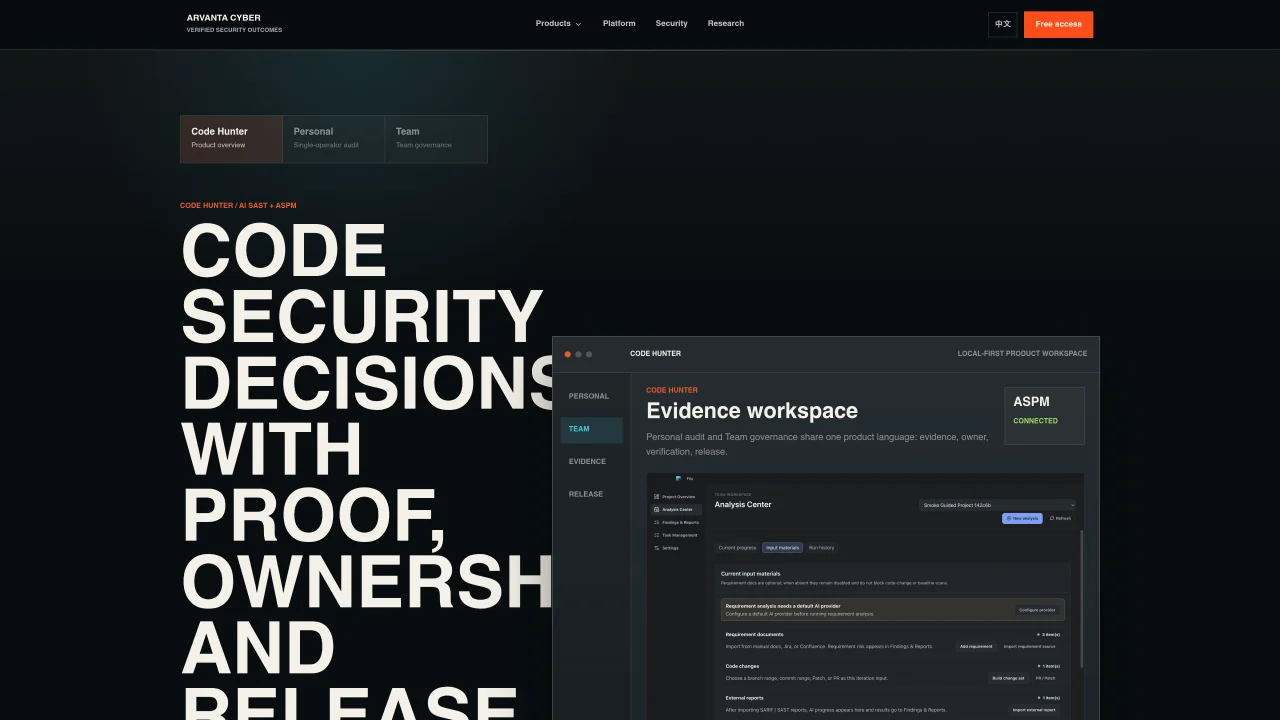
Code Hunter is a local-first desktop application that combines AI-driven static application security testing (SAST) with application security posture management (ASPM). It is designed for security professionals who need to produce audit-grade evidence for code reviews and govern software releases based on verified outcomes. The tool organizes its interface around security decisions such as issue validity, ownership assignment, remediation verification, and release approval. Findings are presented with source-to-sink evidence including data flow paths, failed controls, impact assessments, and remediation guidance. The product supports two editions: Personal for individual auditors and Team for collaborative security governance across multiple projects. Workflows integrate with dependency management, continuous integration systems, and software composition analysis tools to create traceable release gates.
Code Hunter is a local-first desktop application that combines AI-driven static application security testing with application security posture management to help security professionals produce audit-grade evidence for code reviews.
The tool is designed for security professionals, including auditors and governance teams, who need to verify code security and govern software releases based on verified outcomes.
It organizes findings around security decisions such as issue validity, ownership assignment, remediation verification, and release approval, ensuring traceable and auditable workflows.
Yes, it integrates with dependency management, continuous integration systems, and software composition analysis tools to create traceable release gates.
Findings are presented with source-to-sink evidence, including data flow paths, failed controls, impact assessments, and remediation guidance.
Yes, Code Hunter offers two editions: Personal for individual auditors and Team for collaborative security governance across multiple projects.
We use essential cookies to run Aitoolnavio, and optional cookies to analyze traffic and measure our marketing. You choose what we use — optional cookies stay off unless you turn them on. See our Privacy Policy.
One short email a week: fresh tools worth trying, honest takes and the updates that actually matter. No spam, unsubscribe any time.
Privacy-focused AI chatbot that generates uncensored text, code, images, and translations without storing conversations or requiring an account.
AI assistant for safe, reliable productivity with code, collaboration, and integrations.
Automate code, research, and documents using agents.
AI-powered coding platform that uses agents to plan, write, and test software with real-time feedback and verifiable artifacts.
AI-powered code assistant that generates, reviews, optimizes, and debugs code with natural language prompts and editor integrations.
AI-powered IDE for autonomous coding tasks and agentic development workflows
A free web-based AI chatbot and agent for writing, coding, research, and content creation with multilingual support.
Write & run code in 50+ languages, auto-complete with AI, and code faster with an intuitive interface.
AI models that return typed decisions with calibrated confidence for software automation
Practice coding challenges, improve technical skills, get detailed explanations, compare performance with peers.
Professional visual AI engine for node-based image, video, 3D, audio and generative workflows with full control over models and outputs.
An IDE that automates legacy-to-modern code migration using autonomous coding agents.
Matched on what this tool does — grouped by the job you would be replacing.
matches AI SAST with project-aware analysis · Source-to-sink evidence collection · Owner assignment and remediation tracking
Finding code vulnerabilities
Identify errors and vulnerabilities, automate code review and feedback, customize code analysis to meet team needs.
Automate detection of attacks, monitor code security, and generate detailed reports on security posture.
Pinpoint vulnerabilities, automate analysis & reporting, and reduce security costs.
matches Audit-grade reporting · Owner assignment and remediation tracking
Vanta automates compliance certification for SOC 2, HIPAA, ISO 27001, PCI, and GDPR, reducing time from months to weeks.
Offline code security and compliance auditor for Apple Silicon