Frontier-grade Claude models with agentic workflows, strong coding, and enterprise guardrails delivered via developer console, web app, and cloud partners.
Liberra
FreeStarting price
0Popularity
About Liberra
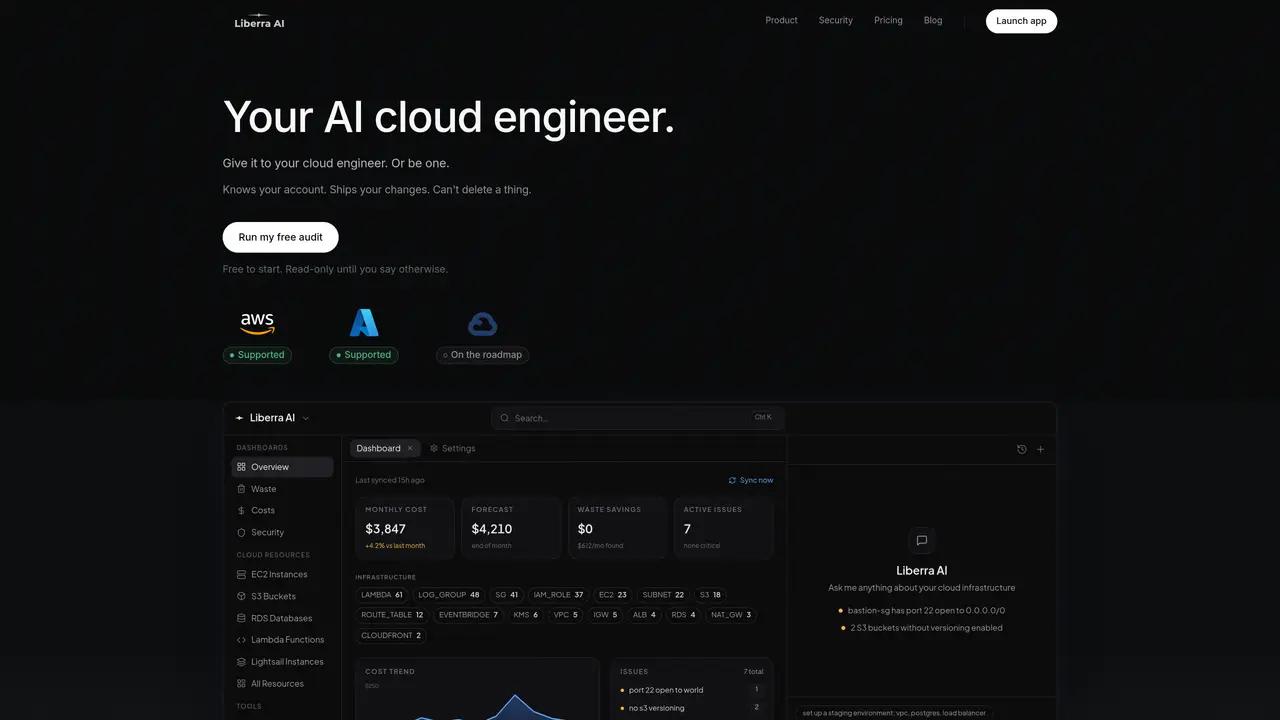
Liberra functions as an AI-driven cloud engineer for AWS and Azure environments. It connects to cloud accounts to provide real-time visibility into infrastructure, costs, and security posture. The tool performs automated scans using Prowler to detect vulnerabilities such as open ports, public databases, unencrypted traffic, and missing backups. It tracks resource usage and cost anomalies, identifying idle or orphaned resources to optimize spending. Liberra can generate Terraform code, deploy infrastructure, and execute commands on live machines with user approval. It maintains a daily inventory of cloud resources across multiple accounts and regions, comparing planned versus actual states to detect drift. The system also maps dependencies and blast radius for resources, tracks changes, and provides explanations for cloud operations. Users can query the AI about any aspect of their cloud environment and receive instant, documented responses.
Key features
- Real-time cloud inventory across multiple accounts
- Automated security scanning for open ports and public resources
- Cost optimization by identifying idle and orphaned resources
- Terraform code generation and deployment
- Live server command execution via chat
- Daily cloud synchronization and change tracking
- Blast radius mapping for resource dependencies
- Cross-cloud comparison and multi-account support
Use cases
- Cloud cost reduction by identifying and removing unused resources
- Security auditing and vulnerability assessment across cloud environments
- Infrastructure automation and deployment using natural language
Pros
- Read-only access by default, requiring explicit approval for changes
- Cross-cloud support for AWS and Azure with unified visibility
- Automated security scanning using Prowler for vulnerability detection
- Daily infrastructure synchronization and cost anomaly tracking
- Terraform integration for infrastructure-as-code deployment
Cons
- No free tier for making changes, only for viewing
- Limited to AWS and Azure with Google Cloud on roadmap
- Monthly subscription required for write access
- No API access mentioned
Frequently asked questions about Liberra
What is Liberra and what does it do?
Liberra functions as an AI-driven cloud engineer for AWS and Azure environments, providing real-time visibility into infrastructure, costs, and security posture. It connects to cloud accounts to perform automated scans, track resource usage, optimize spending, and generate or deploy Terraform code with user approval.
Who is Liberra designed for?
Liberra is designed for cloud engineers, DevOps teams, and organizations managing AWS or Azure environments who need automated infrastructure management, cost optimization, and security monitoring without manual console work.
How does Liberra handle security and safety?
Liberra never deletes resources without explicit user approval and operates on a plan-first basis. It does not store cloud credentials permanently and uses hourly tokens that are revoked immediately upon request. All enforcement code is publicly auditable.
Can Liberra work across multiple cloud providers?
Yes, Liberra supports both AWS and Azure, allowing users to connect and manage multiple accounts and regions across these clouds. It maintains a unified inventory and can answer queries spanning both environments.
What kind of automated scans does Liberra perform?
Liberra performs automated scans using Prowler to detect vulnerabilities such as open ports, public databases, unencrypted traffic, missing backups, stale secrets, and misconfigured resources. It also tracks cost anomalies and resource drift.
How do I get started with Liberra?
Users can start by connecting their AWS or Azure accounts to Liberra, which performs an initial inventory sync. The tool operates in read-only mode by default and requires user approval for any changes or deployments.