Frontier-grade Claude models with agentic workflows, strong coding, and enterprise guardrails delivered via developer console, web app, and cloud partners.
Vibe Check
$9/moStarting price
0Popularity
About Vibe Check
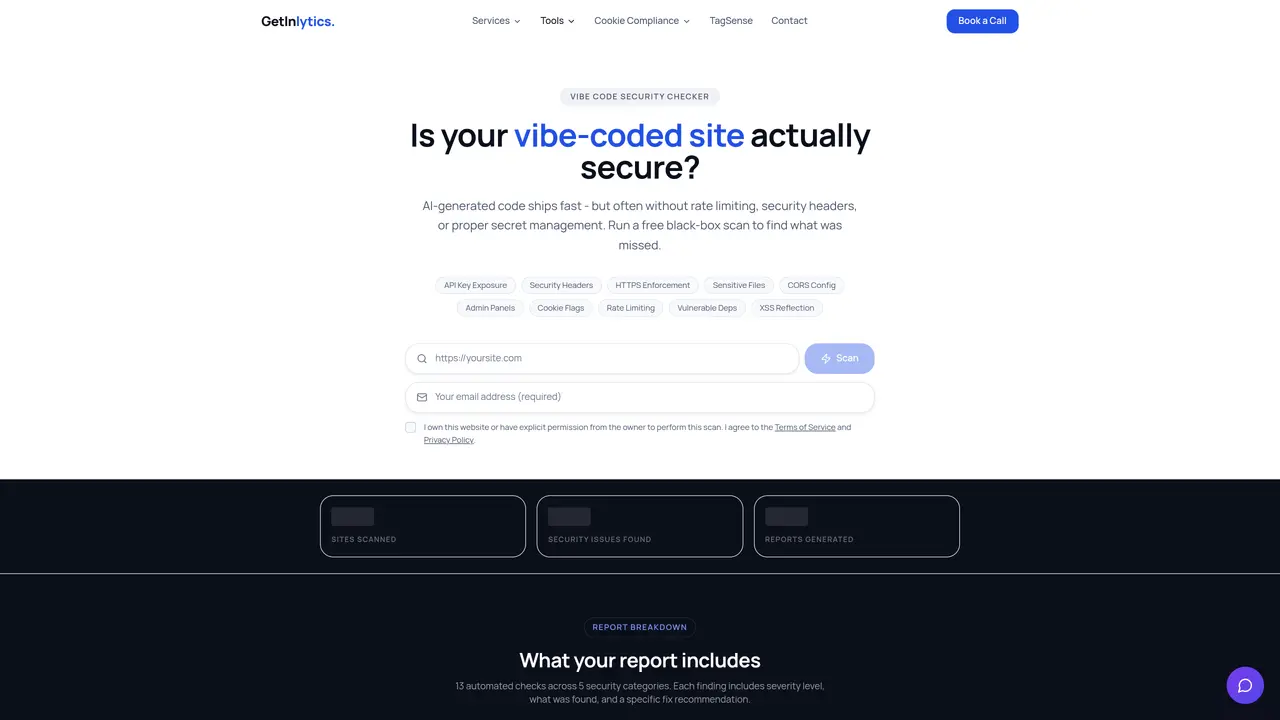
Vibe Check performs automated black-box security scans on public websites to detect vulnerabilities introduced by AI-generated code. It checks for common issues such as exposed API keys, missing security headers, insecure transport settings, and vulnerable dependencies without requiring server access, credentials, or code changes. The tool probes source code for hardcoded secrets, tests sensitive file paths, verifies HTTPS enforcement, and evaluates security headers like CSP and HSTS. It also examines authentication controls, CORS policies, cookie flags, and client-side code risks including outdated libraries and reflected XSS patterns. Each scan generates a 0-100 security score with severity labels and specific fix recommendations for developers or hosting providers. Reports include breakdowns of 13 automated checks across five security categories, prioritizing critical findings such as exposed secrets or missing HTTPS. The scanner is designed for developers, digital marketers, and agency teams who need quick, non-invasive security assessments of websites built with AI tools.
Key features
- Black-box security scanning
- API key exposure detection
- HTTPS and transport security verification
- Security header analysis (CSP, HSTS, X-Frame-Options)
- Sensitive file path probing (.env, .git)
- CORS and cookie flag checks
- Vulnerable dependency detection
- Rate limiting and XSS reflection checks
Use cases
- Quick security audit for AI-generated websites
- Compliance verification for exposed secrets or misconfigured headers
- Developer handoff with actionable fix instructions
Pros
- Non-invasive black-box scanning without server access or credentials
- 13 automated checks covering API keys, HTTPS, headers, CORS, and vulnerable dependencies
- Instant 0-100 security score with severity labels and fix recommendations
- No account required for basic scans
- Free tier available
Cons
- Limited to public URLs and requires ownership or explicit permission
- No free tier for advanced features like multi-region scans or white-label reports
- Scan history limited to 7 days on the lowest paid plan
Frequently asked questions about Vibe Check
Is this scanner safe to run on my site?
Yes. It is a non-invasive black-box scan, performing the same checks as a browser or search engine crawler without exploiting vulnerabilities or altering data.
What does 'vibe-coded' mean and why does it matter for security?
'Vibe-coded' refers to AI-generated code deployed quickly without thorough security review. Such code often lacks rate limiting, proper secret management, or security headers, increasing exposure to common vulnerabilities.
What do I do if the scan flags an API key in my source?
Remove the hardcoded API key from your source code immediately. Rotate the exposed key if it has been compromised and update your application to use environment variables or a secrets manager.
What sensitive file paths does the scanner probe?
The scanner probes paths like .env, .git/HEAD, and config.json that should never be publicly accessible, as exposure can leak credentials, payment keys, or admin passwords.
My CSP header shows as a warning, not a fail. What does that mean?
A warning indicates the CSP header is present but may be misconfigured or overly permissive. Review the header’s directives to ensure they align with your site’s security requirements.
Can I scan a site I do not own?
No. You must own the site or have explicit permission from the owner to perform the scan, as it involves accessing and analyzing public but sensitive aspects of the site.