Frontier-grade Claude models with agentic workflows, strong coding, and enterprise guardrails delivered via developer console, web app, and cloud partners.
flaw.co
$15Starting price
0Popularity
About flaw.co
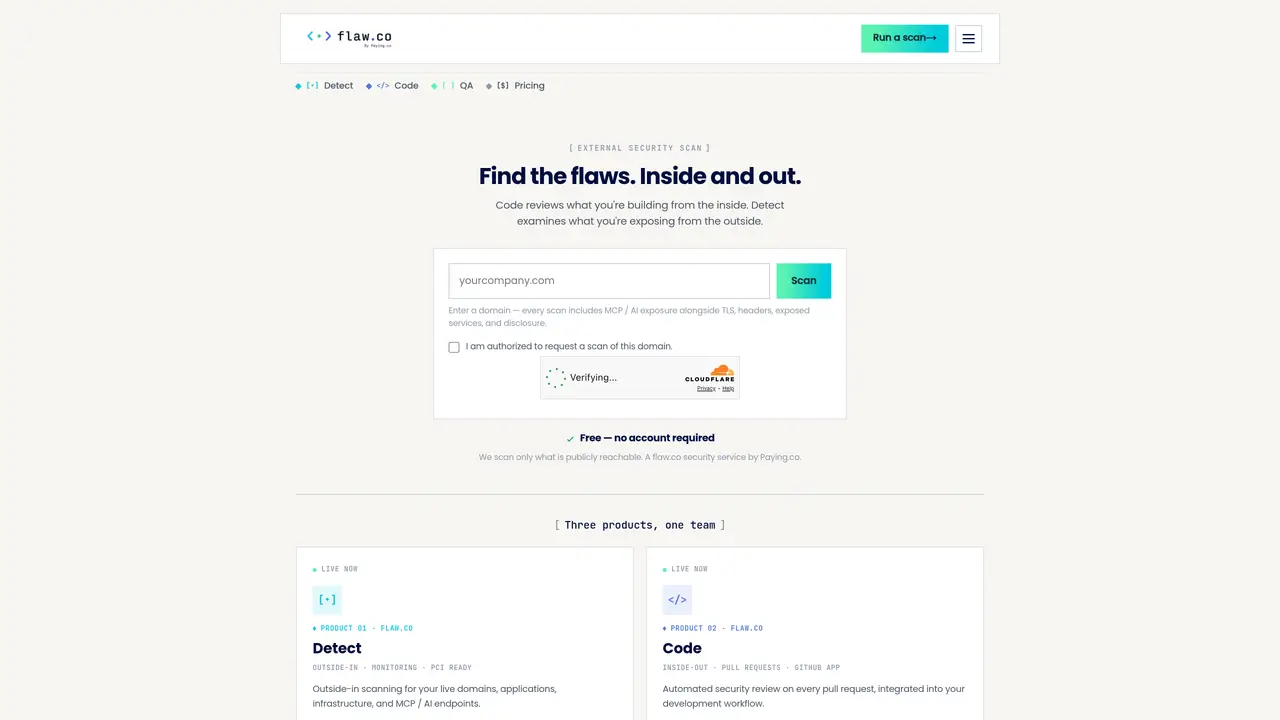
flaw.co provides external security scanning for live domains, applications, and infrastructure, including AI endpoints. It performs passive scans that observe publicly reachable assets such as TLS configurations, HTTP security headers, exposed services, and information disclosure. The tool also detects Model Context Protocol (MCP) and AI exposure by identifying publicly accessible MCP endpoints and assessing their authentication and transport security. For verified domains, an active deep scan tests for vulnerabilities, misconfigurations, and unauthenticated MCP tool-catalog disclosure. flaw.co generates a security grade and detailed findings with remediation steps, including PCI DSS mapping. Continuous monitoring can be scheduled at intervals from weekly to semiannual, with alerts sent only when findings change. The service is designed to be non-intrusive during passive scans and limits active testing to domains under the user’s control.
Key features
- Passive external scanning of TLS, headers, exposed services, and disclosure
- MCP and AI endpoint exposure detection
- Active deep scanning for CVEs, misconfigurations, and unauthenticated MCP disclosure
- PCI readiness grading and PCI DSS requirement mapping
- Continuous monitoring with customizable rescan intervals
- Automated security reviews on GitHub pull requests
- Autonomous exploration testing for live applications
- Change-only email alerts for monitoring
Use cases
- Monitoring external security posture of live domains and infrastructure
- Detecting exposed MCP or AI endpoints accessible from the public internet
- Automated security review of code changes before deployment via GitHub integration
Pros
- Passive external scans available at no cost without requiring an account
- Detects MCP and AI exposure endpoints from an external attacker perspective
- Provides PCI readiness grading and PCI DSS requirement mapping for findings
- Continuous monitoring with change-only email alerts to reduce noise
- Integrates GitHub App for automated code security reviews on pull requests
Cons
- Free tier limited to 5 passive scans per month
- Active deep scans require domain ownership verification
- Code and QA products require paid plans with user limits
- No API or programmatic access mentioned
Frequently asked questions about flaw.co
Is flaw.co free to use?
The passive external security scan is free with no account required, allowing up to 5 scans per month. The Detect tier offers unlimited scans and deep active testing starting at a paid plan.
What does the scan check for?
The passive scan checks TLS/SSL posture, HTTP security headers, exposed services and ports, information disclosure, and MCP/AI exposure. The deep scan adds active testing for CVEs, misconfigurations, and unauthenticated MCP tool-catalog disclosure on verified domains.
What is MCP/AI exposure detection?
MCP (Model Context Protocol) exposure detection identifies publicly reachable MCP endpoints on a domain and assesses their authentication, transport security, and CORS posture. It reveals endpoints that could be exploited by attackers if left unprotected.
Do I need to verify my domain to use flaw.co?
Domain verification is optional for the free passive scan but required for deep active testing. Ownership can be proven via a DNS TXT record or a well-known file to ensure active probes only run on domains you control.
How is the security grade calculated?
Each scan produces a letter grade (A–F) and a 0–100 score based on weighted results across five check families. The grade reflects only the checks that did not pass, with the report showing how many checks ran and how many need attention.
Can flaw.co monitor my domains automatically?
Yes, Detect tier users can schedule automatic rescans at intervals from weekly to semiannual. Alerts are sent only when findings change, such as new vulnerabilities, resolved issues, or grade improvements.