Tesla’s AI stack powers Full Self-Driving, Optimus humanoid robots, and real-world autonomy with neural networks, custom hardware, and Dojo-scale training.
31M visits/mo+5.5%#8 Coding & Development
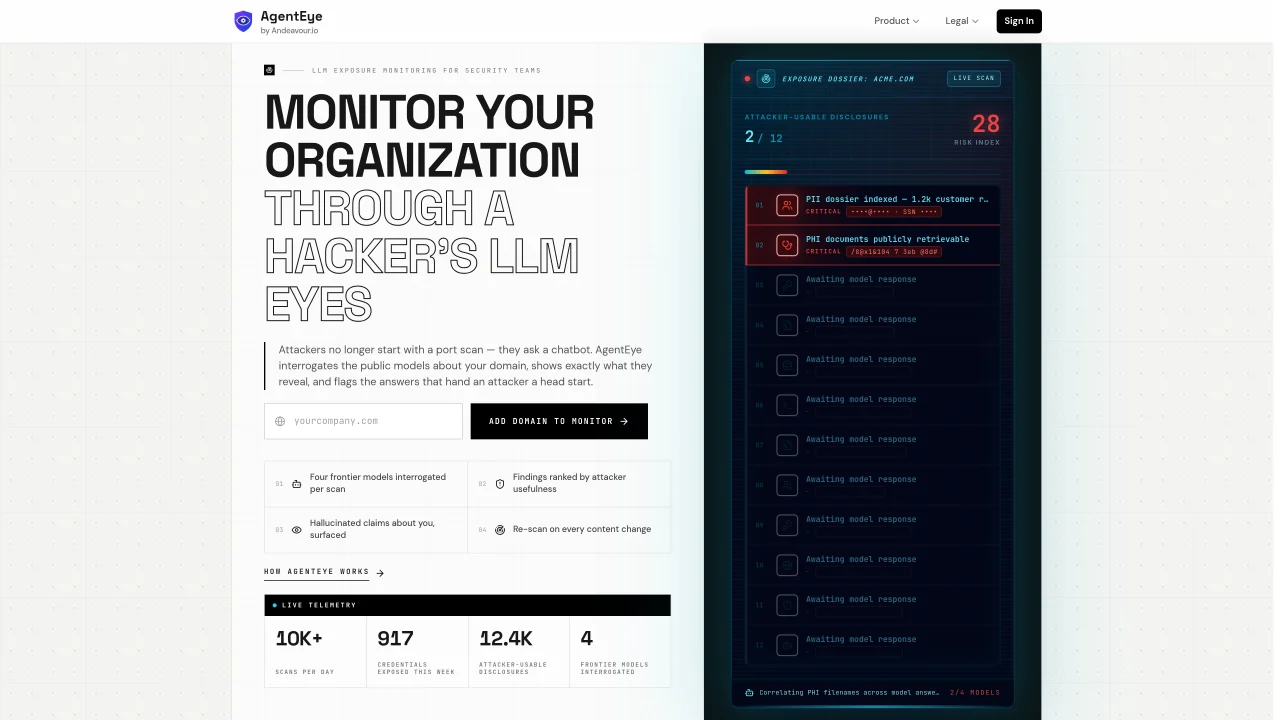
AgentEye is a tool for security teams that interrogates frontier large language models to reveal what information about a domain is publicly accessible. It simulates an attacker’s approach by querying models with prompts designed to extract sensitive data, such as credentials, internal documents, or system details. The tool ranks findings by attacker usefulness and flags disclosures that could provide a head start in a breach. Security teams receive a live telemetry report showing real-time exposure status, including a risk index and a list of disclosed items. Scans are automatically re-run whenever content changes, ensuring continuous monitoring. The system supports multiple frontier models and provides an exposure dossier for each monitored domain.
AgentEye interrogates frontier large language models to reveal what publicly accessible information about a domain could be exploited by an attacker. It simulates an attacker’s approach by querying models with prompts designed to extract sensitive data such as credentials, internal documents, or system details.
AgentEye is designed for security teams and organizations that need to assess their exposure to potential attacks via large language models. It helps identify risks before they can be exploited by malicious actors.
The tool queries large language models with prompts tailored to uncover sensitive information. It ranks findings by attacker usefulness, flags disclosures that could aid a breach, and provides a live telemetry report with a risk index and a list of disclosed items.
Yes, AgentEye supports multiple frontier large language models, allowing security teams to assess exposure across different platforms and providers.
Scans are automatically re-run whenever content changes, ensuring continuous monitoring and up-to-date exposure status for monitored domains.
AgentEye provides a live telemetry report that includes a risk index, a list of disclosed items, and an exposure dossier for each monitored domain, helping security teams prioritize and address risks.
We use essential cookies to run aitoolnavio™, and optional cookies to analyze traffic and measure our marketing. You choose what we use — optional cookies stay off unless you turn them on. See our Privacy Policy.
One short email a week: fresh tools worth trying, honest takes and the updates that actually matter. No spam, unsubscribe any time.
Tesla’s AI stack powers Full Self-Driving, Optimus humanoid robots, and real-world autonomy with neural networks, custom hardware, and Dojo-scale training.
Customize, deploy, and control AI models securely.
Standardize application packaging and execution with portable containers for consistent local and cloud workflows.
AI-first electronic design automation for ICs, advanced packaging, and systems with hardware-assisted acceleration and elastic cloud delivery.
Unified AI-powered platform for real-time monitoring, analytics, and security across cloud infrastructure, applications, and services.
Prevention-first, AI-powered cybersecurity platform protecting networks, clouds, and endpoints with unified controls and autonomous response.
Automate tasks, analyze data, and ensure data security with advanced measures.
Cloud communications platform that lets developers embed SMS, voice, WhatsApp, email, video, verification, and conversational AI via APIs.
AI-powered endpoint security with XDR, cloud or on-prem control, and low system impact for ransomware, email threats, and account takeover prevention.
Automate error tracking, monitor application performance, and gain insights with advanced analytics.
Identify stolen identities, uncover copyright infringements, and find unauthorized use of images with precision.
Instant threat detection and response, AI-powered prevention, unified dashboard for full visibility and control.
Matched on what this tool does — grouped by the job you would be replacing.
matches Monitors public LLM exposure of an organization's domain · Interrogates four frontier LLM models per scan · Ranks exposed data by attacker usefulness
Audits websites for AI agent compatibility by simulating real agent tasks
External security and PCI readiness scanning for domains and AI endpoints
Desktop tool that monitors and reports on local machine state and agent activity