Frontier-grade Claude models with agentic workflows, strong coding, and enterprise guardrails delivered via developer console, web app, and cloud partners.
Guile
0Popularity
About Guile
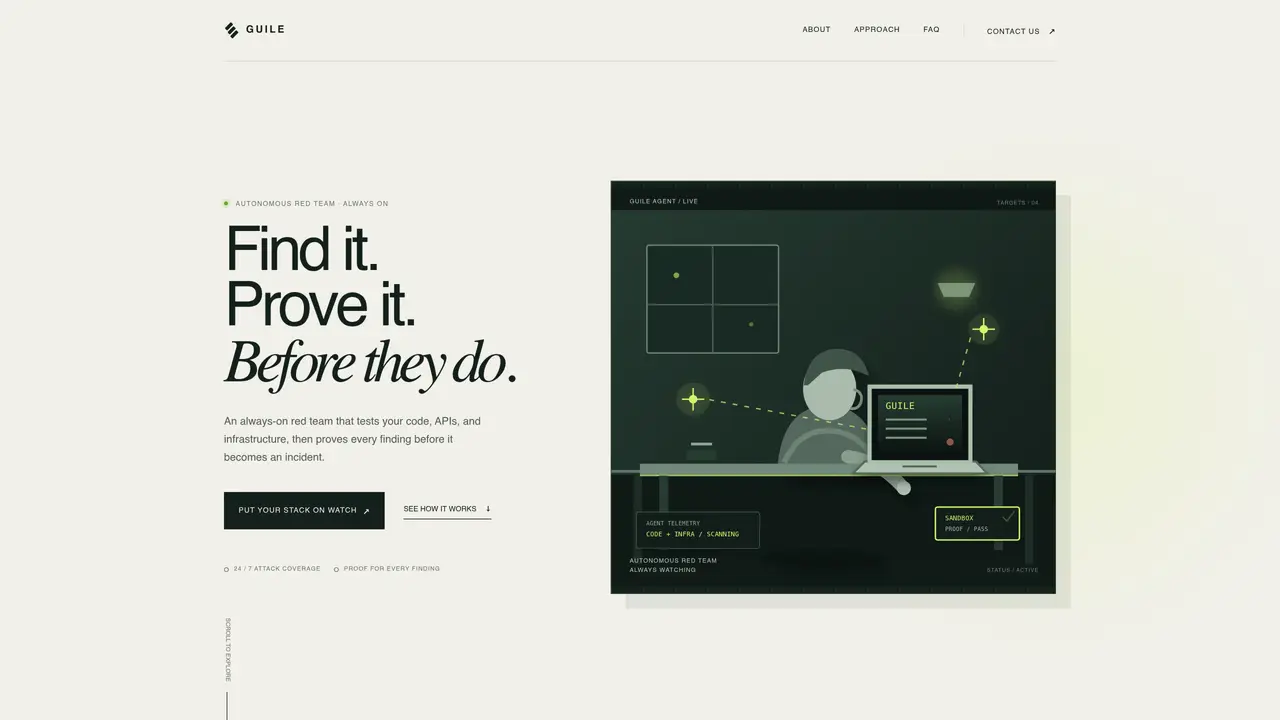
Guile provides always-on red teaming that continuously tests software stacks across code, REST and GraphQL APIs, web applications, infrastructure and cloud environments. It autonomously explores attack paths as systems evolve, validating each finding with proof-of-exploit evidence that shows the path, impact and affected assets. The platform then delivers clear reproduction steps and prioritized remediation guidance to engineering teams. Guile is designed for organizations shipping software rapidly, replacing periodic testing with continuous offensive coverage that adapts to changing environments. It integrates into existing workflows without replacing security teams, providing actionable insights while teams retain control over risk decisions and fixes.
Key features
- Continuous autonomous attack simulation
- Proof-of-exploit validation for findings
- Full-stack coverage including code, APIs, apps, infrastructure and cloud
- Clear remediation steps and prioritization
- Real-time attack path discovery
- REST and GraphQL API testing
- Web application flow tracing
- Cloud configuration assessment
Use cases
- Continuous security validation for CI/CD pipelines
- Proactive threat detection in rapidly changing environments
- Prioritized remediation guidance for engineering teams
Pros
- Continuous 24/7 testing across full stack
- Proof-of-exploit evidence for every finding
- Clear remediation steps for engineering teams
- Adapts coverage to changing software environments
- Integrates code, APIs, apps, infrastructure and cloud
Cons
- No free tier or public pricing
- Requires integration with existing stack
- No mention of API access for third-party tools
- Limited to supported programming languages and frameworks
Frequently asked questions about Guile
What does Guile test?
Guile provides full-coverage pentesting across code, REST and GraphQL APIs, web applications, infrastructure, and cloud environments.
What does proof-of-exploit mean?
Every validated finding includes evidence of the attack path, what was reached, and why the issue matters so your team can reproduce and prioritize it.
How often does Guile run?
Guile works continuously, helping you find and fix vulnerabilities 24/7 as your product, infrastructure, and cloud environment change.
Will Guile replace our security team?
Guile gives security and engineering teams always-on offensive coverage while people stay in control of risk decisions and remediation.
How does Guile integrate into existing workflows?
Guile integrates into existing workflows without replacing security teams, providing actionable insights while teams retain control over risk decisions and fixes.
What kind of remediation guidance does Guile provide?
Guile delivers clear reproduction steps and prioritized remediation guidance to engineering teams after validating each finding.