Finding code vulnerabilities
801K visits/mo-5.7%#97 Coding & Development
Static security scanner for AI-built applications identifying vulnerabilities before deployment
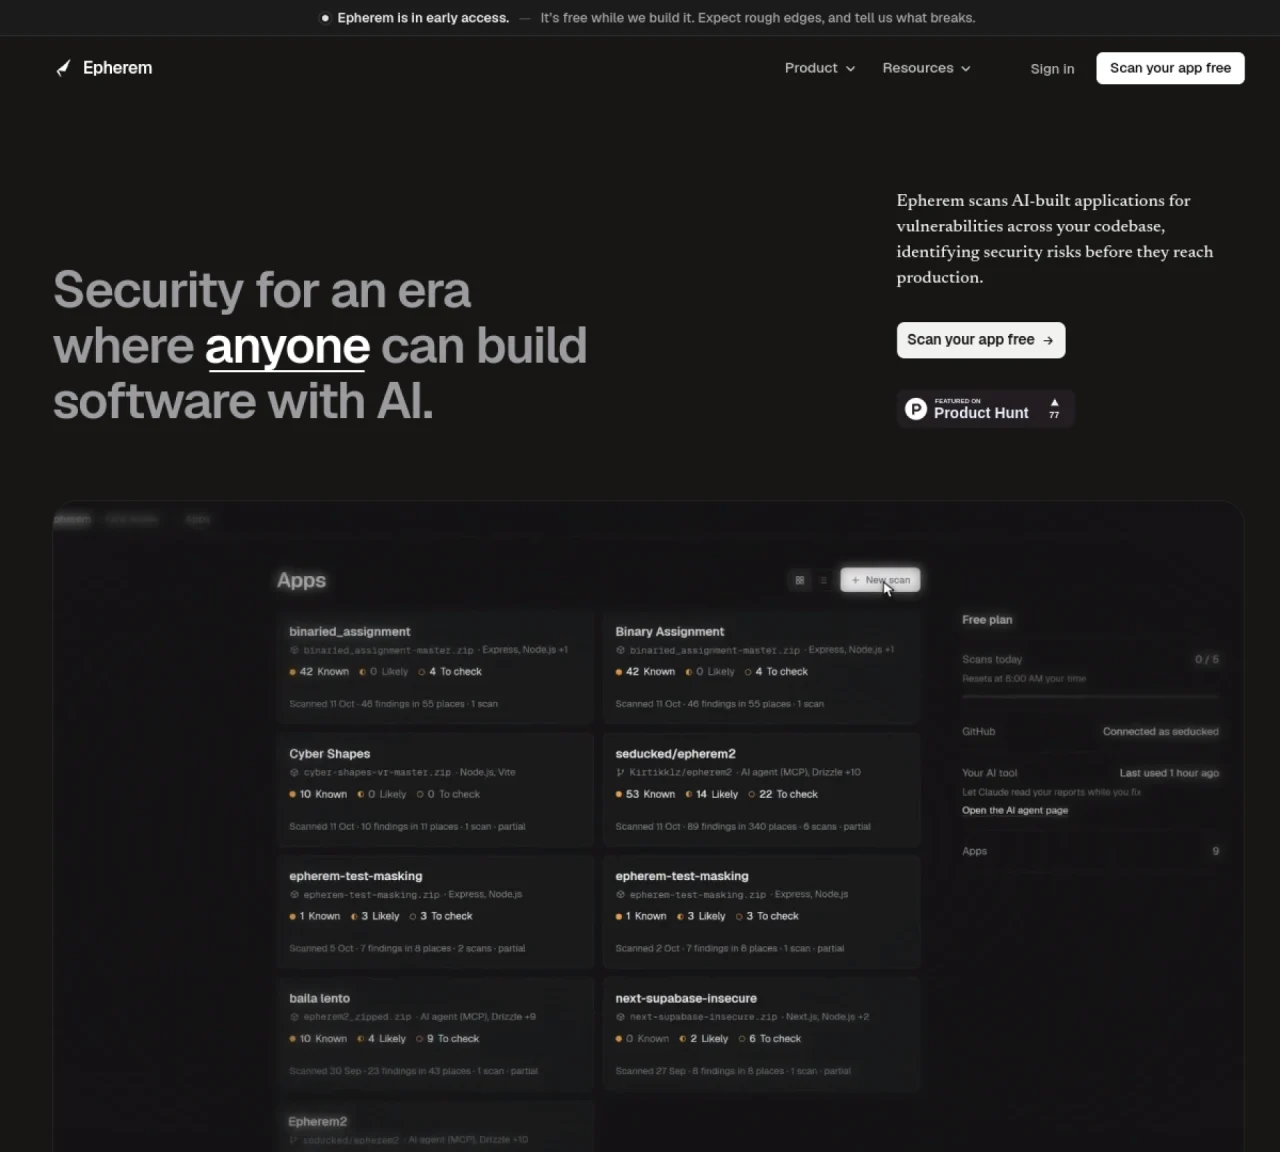
Epherem scans applications built with AI development tools such as Lovable, Bolt, v0, Replit, Cursor and Claude Code for security vulnerabilities across codebases, settings files and package dependencies. The tool analyzes projects uploaded as ZIP files or connected via GitHub without executing the application itself. It performs 55 checks including detection of hardcoded secrets, SQL injection risks, missing CSRF protection, unsafe input handling and package vulnerabilities against published advisories. Each finding is categorized as known issues, likely issues or findings needing manual verification, with exact file locations and line numbers provided. Reports explain what is wrong, what an attacker could do, and how to fix it, including prompts compatible with Cursor, Lovable or Claude Code for automated remediation. The scanner distinguishes between code it analyzed and elements it could not read, ensuring reports never falsely claim a clean scan.
Epherem is a free security scanner designed for applications built using AI development tools like Lovable, Bolt, v0, Replit, Cursor, and Claude Code. It scans codebases, settings files, and package dependencies for security vulnerabilities without executing the application itself.
Epherem is ideal for developers and teams building software with AI tools who want to identify and remediate security risks before their applications reach production. It is particularly useful for those using platforms like Cursor, Lovable, or Claude Code.
Users can upload their project as a ZIP file or connect via GitHub. Epherem reads the code, settings files, and package list to perform 55 checks for vulnerabilities such as hardcoded secrets, SQL injection risks, and missing CSRF protection.
Epherem detects a range of vulnerabilities including hardcoded secrets, SQL injection risks, missing CSRF protection, unsafe input handling, and package vulnerabilities by checking against published advisories.
Findings are categorized as known issues (published advisories), likely issues (risky code detected by the scanner), findings needing manual verification, and elements the scanner could not read. This ensures reports never falsely claim a clean scan.
Yes, each finding includes a prompt compatible with AI tools like Cursor, Lovable, or Claude Code to assist with automated remediation. Users can paste the prompt into their AI tool to generate fixes, though some actions like rotating leaked keys must be done manually.
We use essential cookies to run Aitoolnavio, and optional cookies to analyze traffic and measure our marketing. You choose what we use — optional cookies stay off unless you turn them on. See our Privacy Policy.
One short email a week: fresh tools worth trying, honest takes and the updates that actually matter. No spam, unsubscribe any time.
Matched on what this tool does — grouped by the job you would be replacing.
matches 55 vulnerability checks · ZIP or GitHub project upload · Package advisory matching
Finding code vulnerabilities
Static analysis tool that predicts app failures before launch
Static analysis tool that scans AI-built applications for security flaws before deployment
AI-assisted static analysis and application security posture management with evidence tracking
matches AI System Prompt Security Scanner · Prompt vulnerability scanning · Strength categorization (weak, medium, strong)
matches Free black-box security scanner for AI-generated websites · Black-box security scanning · API key exposure detection
Free AI system prompt vulnerability scanner
AI-powered website security scanner with plain-English risk explanations and free remediation guidance
Free black-box security scanner for AI-generated websites
Website security scanner detecting vulnerabilities and compliance gaps
Customize, deploy, and control AI models securely.
AI-first electronic design automation for ICs, advanced packaging, and systems with hardware-assisted acceleration and elastic cloud delivery.
Standardize application packaging and execution with portable containers for consistent local and cloud workflows.
Cloud communications platform that lets developers embed SMS, voice, WhatsApp, email, video, verification, and conversational AI via APIs.
Unified AI-powered platform for real-time monitoring, analytics, and security across cloud infrastructure, applications, and services.
AI-powered endpoint security with XDR, cloud or on-prem control, and low system impact for ransomware, email threats, and account takeover prevention.
Prevention-first, AI-powered cybersecurity platform protecting networks, clouds, and endpoints with unified controls and autonomous response.
Identify stolen identities, uncover copyright infringements, and find unauthorized use of images with precision.
Automate tasks, analyze data, and ensure data security with advanced measures.
Automate error tracking, monitor application performance, and gain insights with advanced analytics.
Instant threat detection and response, AI-powered prevention, unified dashboard for full visibility and control.
Verify customer identity, automate compliance checks, reduce costs, and manage customer data securely while ensuring data privacy.