Runtime platform for deploying AI workloads, databases and services across clouds or on-premises
303K visits/mo-18%#168 Coding & Development
On-call automation for regulated enterprises that fixes incidents with human approval
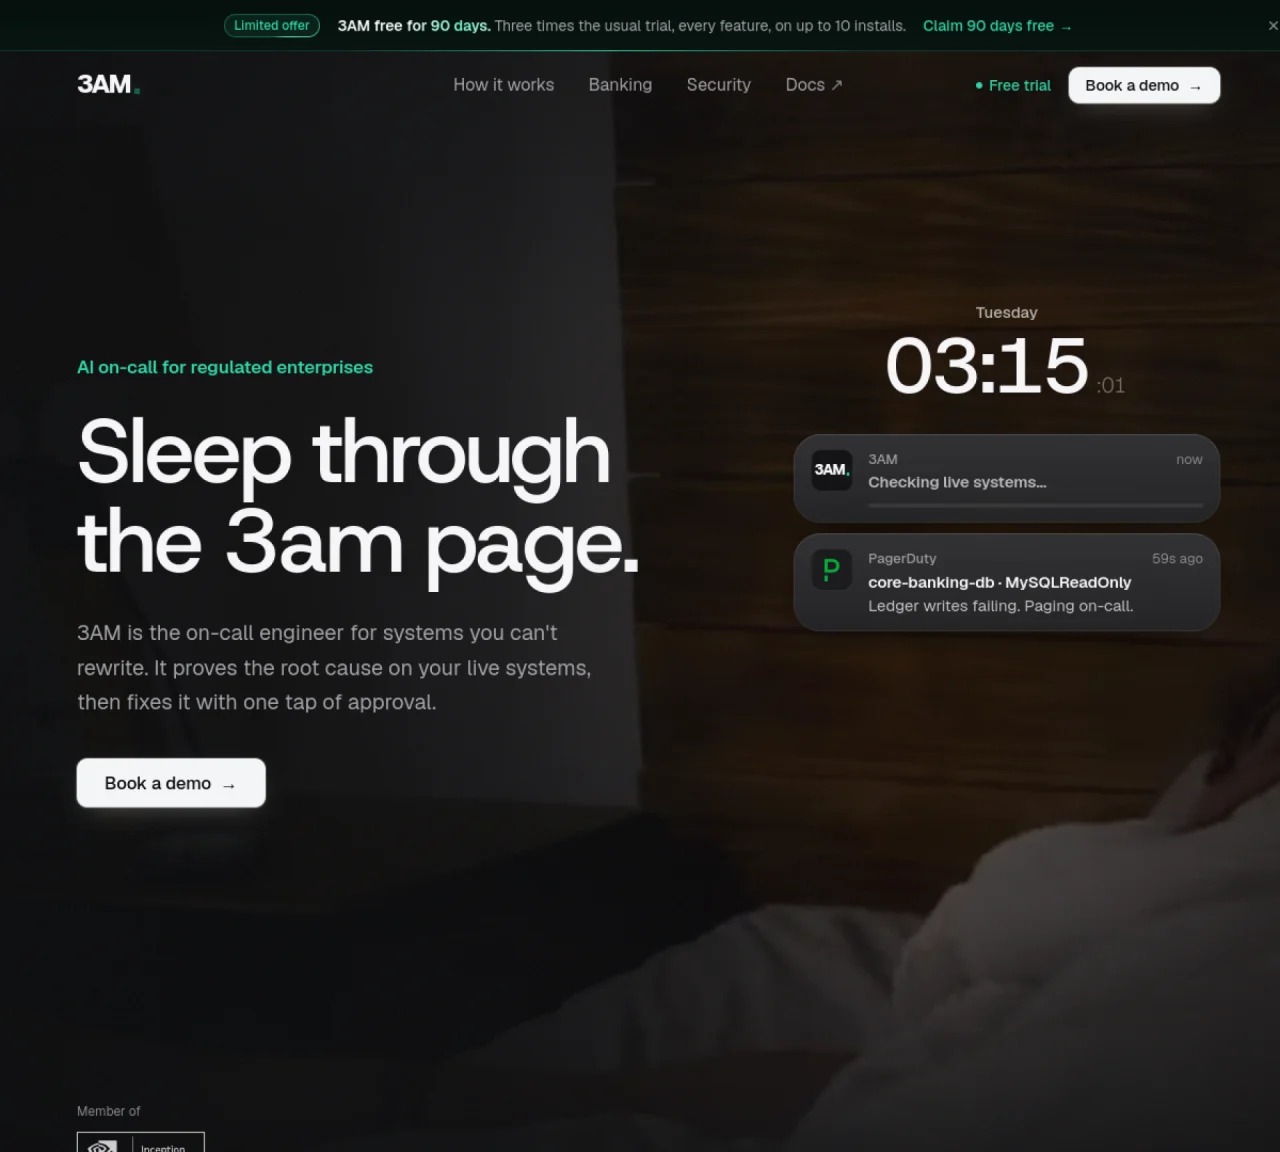
3AM acts as an on-call engineer for systems that cannot be rewritten, such as legacy databases or critical infrastructure. It integrates with existing monitoring and alerting tools to analyze incidents, prove root causes using live system checks, and propose fixes. Each action requires explicit human approval before execution, ensuring safety in regulated environments. The system operates on-premises without inbound ports, maintaining network isolation while providing a tamper-evident audit trail. It supports dry-run rehearsals of fixes and allows teams to grant autonomy at the service level, enabling faster incident resolution while preserving control. Every decision, check, and action is recorded in a cryptographically signed ledger for compliance and auditing purposes.
3AM acts as an on-call engineer for systems that cannot be rewritten, such as legacy databases or critical infrastructure. It integrates with existing monitoring and alerting tools to analyze incidents, prove root causes using live system checks, and propose fixes with explicit human approval before execution.
3AM is designed for regulated enterprises that require safe, controlled automation for incident response in environments where systems cannot be easily modified. It suits teams managing legacy databases, core banking systems, or other critical infrastructure.
3AM operates on-premises without inbound ports, maintaining network isolation. Every action requires explicit human approval, and all decisions, checks, and actions are recorded in a cryptographically signed ledger for compliance and auditing purposes.
3AM connects to tools such as Prometheus, Grafana, Datadog, PagerDuty, Jira, GitHub, GitLab, Bitbucket, Kubernetes, MySQL, PostgreSQL, Oracle, Slack, Symphony, and Twilio. It reads alerts and system metrics to diagnose and propose fixes.
No, 3AM requires explicit human approval for every action. It can operate in shadow mode initially, but autonomy must be explicitly granted at the service level, and actions still require approval before execution.
3AM records every signal, check, approval, and action in a tamper-evident audit ledger that is hash-chained and cryptographically signed. This ledger is exportable to SIEM systems for compliance and verification by auditors.
We use essential cookies to run aitoolnavio™, and optional cookies to analyze traffic and measure our marketing. You choose what we use — optional cookies stay off unless you turn them on. See our Privacy Policy.
One short email a week: fresh tools worth trying, honest takes and the updates that actually matter. No spam, unsubscribe any time.
Runtime platform for deploying AI workloads, databases and services across clouds or on-premises
Hardware and software stack for high-performance AI inference workloads
Enterprise AI platform for autonomous agent orchestration and real-time data pipelines
Cloud platform providing on-demand and reserved GPU clusters for AI training, fine-tuning and inference
Virtual servers with dedicated NVIDIA GPU acceleration for AI workloads
Unified API gateway for routing, comparing, and operating across 200+ AI models via a single
Local LLM routing layer for connecting models and tools
Tracks and attributes AI costs across multiple LLM providers with budget controls
Framework for adding AI agents to products with built-in infrastructure
Peer-to-peer AI inference marketplace for running and monetizing models
Marketplace for AI agent tools using the Model Context Protocol standard
Managed deployment platform that turns git pushes into live web apps with databases and storage
Matched on what this tool does — grouped by the job you would be replacing.
matches Proves root cause using live system checks · Dry-run rehearsals for all proposed fixes · Human approval required before executing actions
An AI incident management platform that autonomously investigates alerts, finds root causes, and suggests fixes for engineering and SRE teams.
AI SRE platform that continuously analyzes Kubernetes and cloud infrastructure to auto-investigate alerts and propose remediation steps.
Autonomously triages and roots cause alerts in complex infrastructures.
matches Tamper-evident audit ledger with hash-chaining · Incident timeline replay with ledger events
matches Human approval required before executing actions · Service-level autonomy control
NexArt generates tamper-proof, cryptographically signed records of AI executions for audits and compliance in regulated industries.
Creates tamper-evident audit logs of AI agent actions without storing sensitive data
Control plane and tamper-evident audit ledger for governing AI agents
Governance layer that validates AI agent actions before they update business systems
Control plane for autonomous AI agents managing financial actions
Pre-execution governance layer that verifies AI-agent actions before payment rails are triggered
Policy engine that authorizes AI agent spend in real time with granular rules and audit trails
Governance layer that checks identity, authority and policy before autonomous systems execute consequential